A discreet purchase-review framework for UNA buyers, separating advertised security services from the credential administration, vendor safeguards, and resident-data policies that deserve written confirmation.
At Una Residences Brickell, the purchase conversation extends beyond the waterfront setting to a quieter consideration: who controls access, who can see resident information, and how long that information remains available. For a buyer who values discretion, these are practical components of ownership, not merely technical details.
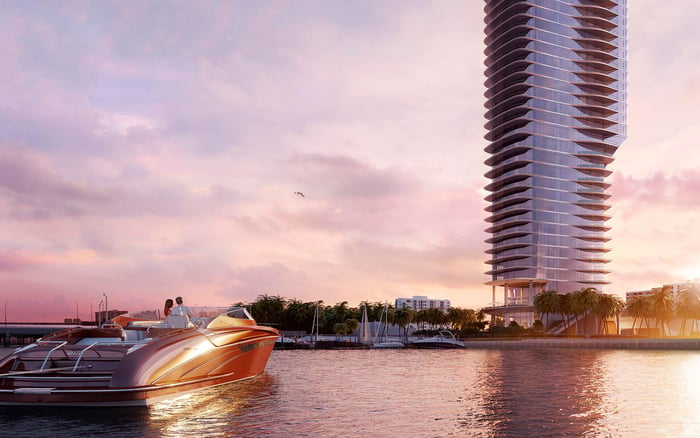
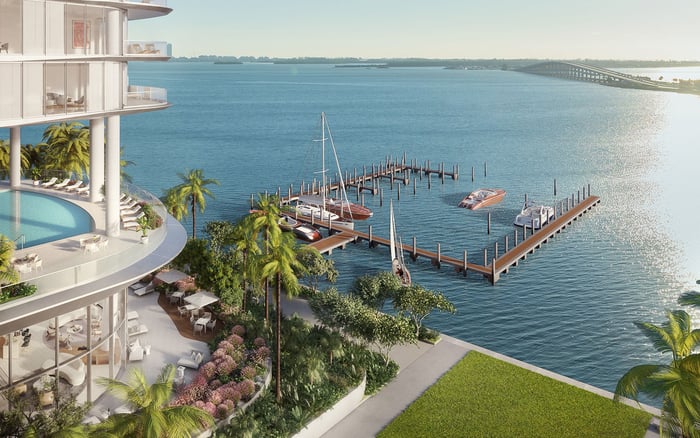
UNA is a waterfront condominium in Miami’s Brickell neighborhood. Its advertised amenities include 24-hour concierge and security, private elevator entries, a private marina, valet service, and secured underground parking. Those features warrant a closer look at access governance, but they do not establish specific credential technologies or cybersecurity safeguards.
The distinction is essential: a security service describes an offering; a written policy defines authority and accountability. Publicly disclosed details do not establish UNA’s cybersecurity architecture, credential administrator, or resident-data-retention schedule. That does not mean safeguards are absent. It means buyers should seek confirmation rather than infer protections from amenity language.
Begin with a system inventory. Ask which manufacturers and vendors support building entry, elevator authorization, garage access, and amenity access. Request the credential types actually used, without assuming that access depends on cards, phones, biometrics, or any other technology.
Then identify the administrator for each system. Does authority rest with the association, property manager, security contractor, technology vendor, or several parties with different permissions? Request a responsibility matrix covering credential issuance, changes, revocation, and emergency intervention. A general statement that security manages access is less useful than knowing who can authorize a change and who reviews it.
Ask how lost credentials are disabled, how replacements are approved, and whether temporary permissions expire automatically. Procedures for staff, vendors, household employees, and visitors should each be clearly explained. These are diligence questions, not descriptions of UNA’s current configuration.
For buyers also considering Cipriani Residences Brickell, the same questions provide a consistent comparison framework without suggesting that either building uses equivalent systems or policies.
Private elevator entries warrant a focused review of authorization. Ask how an invited guest reaches the residence, who grants permission, and whether access is limited by destination or time. Request an explanation of delivery, maintenance, and emergency-access procedures, including how exceptions are approved and recorded.
The central question is not simply whether a residence has a private arrival, but how access to that arrival is governed. Ask whether staff privileges differ from resident privileges and how permissions change when an employee, contractor, or household arrangement changes.
Buyers need not request passwords, live credentials, or sensitive system diagrams. A non-sensitive description of roles, approval steps, and revocation procedures can support purchase review while respecting the building’s security boundaries.
UNA’s advertised marina, valet service, and secured underground parking raise distinct access questions. Ask whether those services share a credential system with residential entry or operate separately. Do not assume a single policy covers every point of arrival.
For the marina, request guest and service-provider authorization procedures. For valet, ask what information is collected and which parties may retrieve it. For parking, establish whether vehicle identifiers or license-plate information are collected before evaluating retention. Secured parking alone does not confirm license-plate recognition technology.
Apply the same approach to amenity and visitor records. Ask which records are created, why each is needed, and whether information is shared across systems. A useful response distinguishes service delivery from the storage of identifiable resident activity.
Request separate retention schedules for elevator and entry logs, visitor registrations, garage records, license-plate data if collected, valet records, marina records, and surveillance footage. For each category, seek the retention period, storage location, authorized users, deletion process, and procedure for preserving material when an incident requires it.
UNA’s publicly disclosed details do not specify these periods or establish whether surveillance footage is stored locally, in the cloud, or through a third-party monitoring provider. Ask directly, including whether copies or backups remain after routine deletion.
Florida condominium law generally requires official association records to be maintained within Florida for at least seven years, subject to exceptions. Specified core records, including governing documents, bylaws, articles, rules, and minute books, must be maintained permanently from the association’s inception.
Neither rule should be treated as an automatic retention requirement for every access log or camera recording. Counsel should establish the applicable classification and verify the statutory version applicable to the transaction before a buyer accepts a blanket seven-year answer.
Unit owners generally may inspect association official records within 10 working days after receipt of a written request, subject to statutory exceptions. Prospective buyers should not assume they have the same rights before ownership.
Coordinate document requests through the seller, authorized representatives, and transaction counsel. Ask for policies and relevant contract provisions rather than unrestricted access to resident histories. Certain sensitive personal information and electronic security measures, including passwords, are excluded from ordinary owner-records inspection.
For a purchaser comparing UNA with The Residences at 1428 Brickell, a consistent request for non-sensitive governance documents is more meaningful than a comparison of broad security descriptions alone.
Ask where vendors host information, who can access it, whether subcontractors are involved, and which party handles incident response. Request the contractual allocation of breach obligations, deletion requirements, and responsibility when a vendor relationship ends. Seek confirmation of administrator-account protections and the process for reviewing access changes.
Biometric access control is not confirmed for UNA. Florida’s statutory definition includes automatically measured fingerprints, voiceprints, retinas, irises, and other unique biological characteristics used to identify someone. If collection is confirmed, request enrollment, consent, retention, and deletion policies. The definition alone does not establish the obligations applicable to a particular system.
Florida’s breach-notification statute requires covered entities and third-party agents to take reasonable measures to dispose of customer records containing personal information when retention ends. Disposal must render that information unreadable or undecipherable. Ask how operating policies and vendor contracts address applicable requirements.
Distinguish developer-installed technology from the association’s post-turnover policies and contracts. Ask which documents govern today, what may change, and who will administer the systems after any ownership or management transition.
Before closing, seek written answers on credential authority, retention schedules, vendor responsibilities, and move-out deactivation. For a second-home purchase, include procedures for household staff and guests during the owner’s absence. A concise schedule of unresolved items can help counsel separate material concerns from routine follow-up.
The objective is not unrestricted access to security infrastructure. It is confidence that the people operating the building can explain how permissions and personal information are governed.
For a discreet approach to South Florida purchase planning, explore MILLION.
If branded residences are on your mind — as a home or as an allocation — we would be glad to share what we are seeing, privately.
Begin a quiet conversationPublished descriptions advertise 24-hour concierge and security services. Those descriptions do not establish specific credential technologies or cybersecurity controls.
Biometric access control is not confirmed in the reviewed public details. Buyers should request confirmation rather than infer its use from security marketing.
Publicly disclosed details do not identify the credential administrator. Ask whether authority rests with the association, manager, security contractor, vendor, or multiple parties.
Residences are described as having private elevator entries. Buyers should clarify guest authorization, staff permissions, exception handling, and credential revocation.
Request separate schedules for access logs, visitor registrations, garage records, valet records, marina records, and surveillance footage. Include license-plate data if collection is confirmed.
No automatic seven-year requirement should be assumed for every access log or recording. The applicable records classification and statutory exceptions must be established.
Prospective buyers should not assume they have unit-owner inspection rights. Coordinate requests through the seller, authorized representatives, and transaction counsel.
No. Florida condominium law excludes certain sensitive personal information and electronic security measures, including passwords, from ordinary owner-records inspection.
Publicly disclosed details do not establish whether footage is stored locally, in the cloud, or by a third-party provider. Request storage, access, backup, and deletion information.
Ask how applicable disposal requirements are implemented in policies and vendor contracts. Florida’s breach-notification statute requires covered entities and third-party agents to use disposal measures that render personal information unreadable or undecipherable when retention ends.