A discreet pre-purchase checklist for Frida Kahlo Wynwood Residences, focused on access credentials, movement-history controls, cybersecurity accountability, and the separation of any medical-service data from building records.
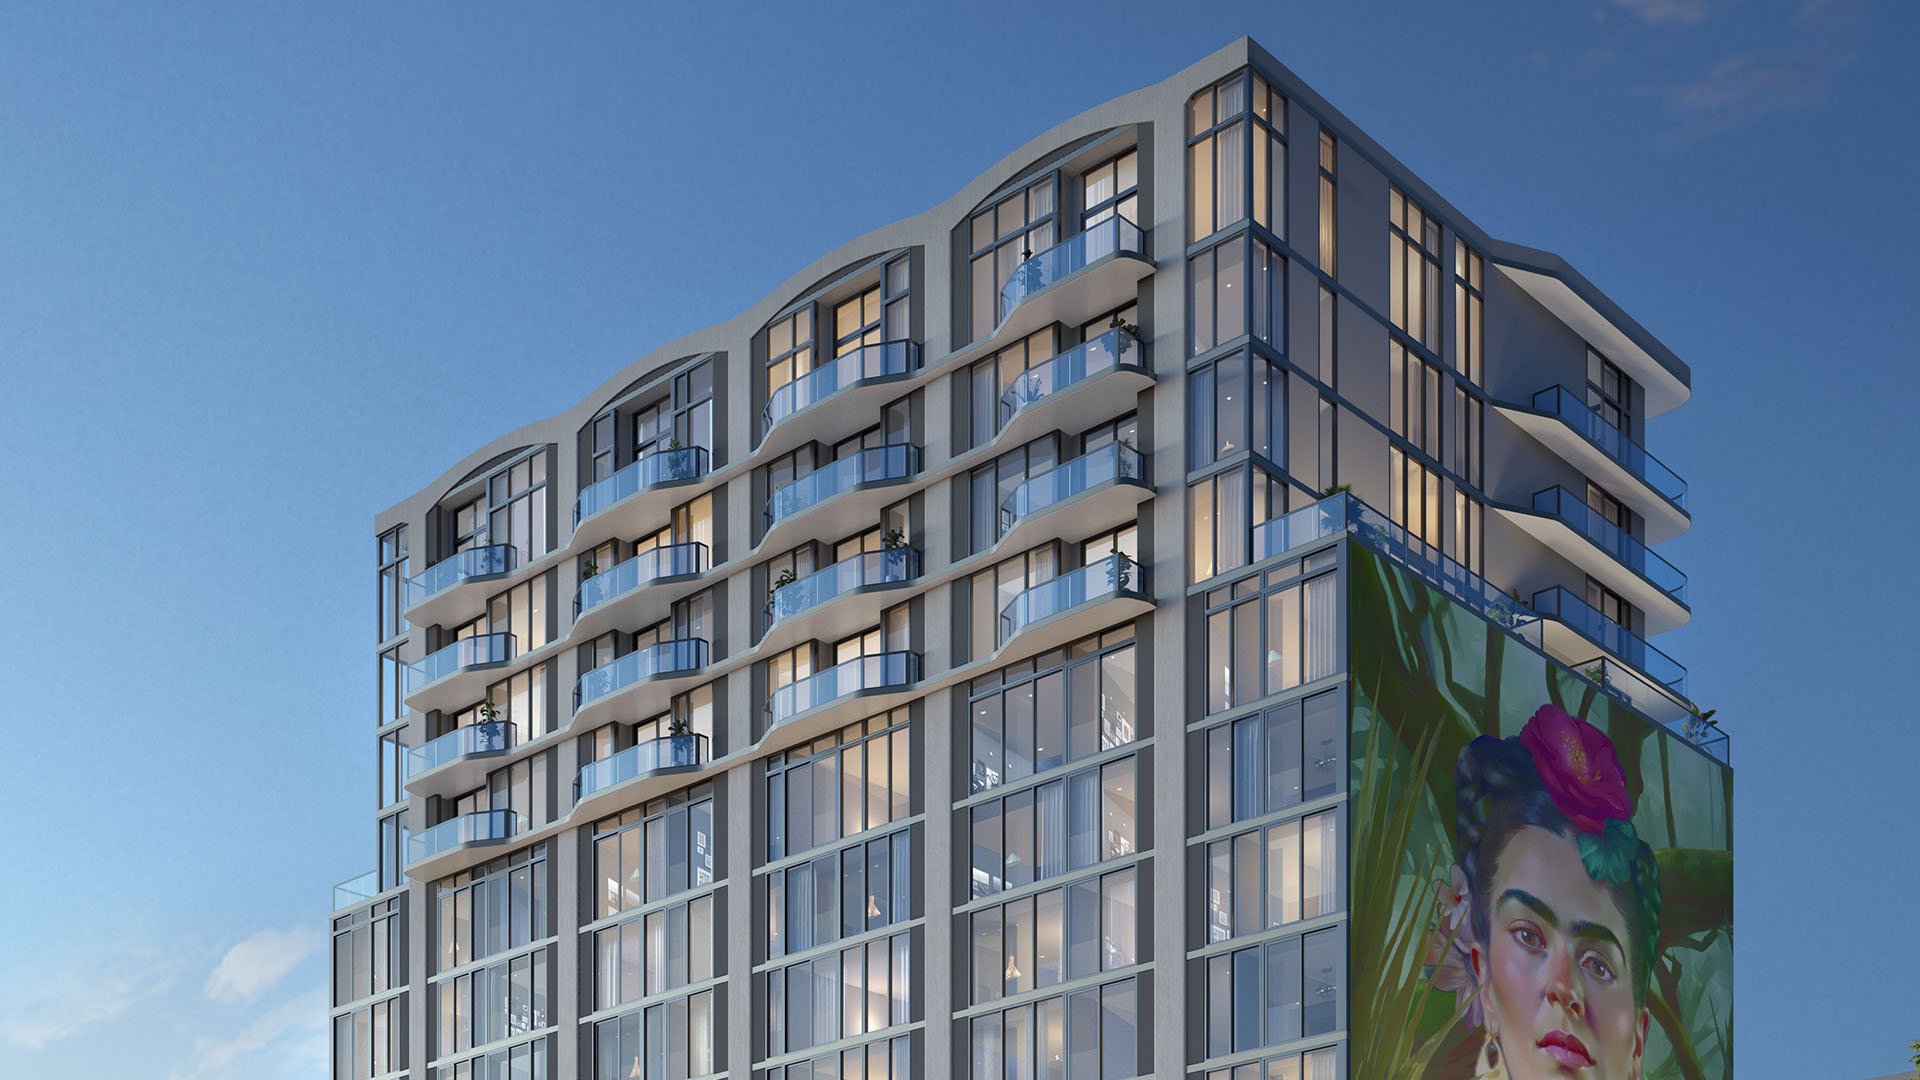
Discretion deserves the same attention as a residence’s layout and finishes. For a buyer considering Frida Kahlo Wynwood Residences, that means asking not only how entry is controlled, but who can reconstruct a resident’s movements, how long those records remain available, and who is accountable for protecting them.
Several underlying systems and their governing policies remain unverified here. That is a due-diligence question, not evidence of a breach, unlawful processing, or inadequate security. Policies and technical evidence may be available privately. The objective is to replace broad assurances with written answers before making a purchase commitment.
Begin with a system inventory. The access-control vendor, camera platform, resident-app provider, and cloud-hosting location remain unidentified in this review. Whether entry uses key fobs, mobile credentials, facial recognition, fingerprints, license-plate recognition, or smart locks also remains unconfirmed.
Ask the seller or authorized project representative to distinguish confirmed specifications from proposed selections. A useful response should identify each system’s purpose, the information it collects, where that information is stored, and which parties administer it. Request a responsible contact for unresolved selections and a process for receiving updates.
Keep the inquiry operational rather than promotional:
Request a list of information required from residents, guests, household staff, and service providers.
Identify which systems exchange information and which remain separate.
Establish who can create, suspend, replace, or revoke a credential.
Confirm entry arrangements during an outage or lost-device event.
These are requests for verification, not descriptions of confirmed project features.
A project-specific access-log retention period and a policy governing retrieval and disclosure of residents’ movement histories remain unverified here. The critical distinction is between granting someone entry and allowing someone else to search that person’s history.
Request a permissions matrix specifying which roles may view, search, export, or disclose access records. Ask whether searches and exports are themselves logged, whether staff access is reviewed, and how privileges are removed when an employee or contractor leaves. If remote vendor access is permitted, ask who authorizes it and how it is supervised.
Disclosure deserves its own written procedure. Ask how requests from owners, household members, insurers, attorneys, and public authorities are evaluated, and who decides whether disclosure is appropriate. Do not assume that ownership entitles a resident to inspect another resident’s movements.
For a buyer also considering The Residences at 1428 Brickell, the same questionnaire can bring greater discipline to a Brickell comparison. It does not imply that either property uses the same systems or follows the same policies.
Ask for a schedule that separates access events, camera footage, visitor records, resident profiles, and any biometric information, if collected. For each category, request the purpose, retention period, deletion trigger, and party responsible for implementation.
A useful schedule should also explain exceptions. Ask how incident preservation, legal holds, backups, and exported copies affect deletion. If a vendor keeps a separate copy, clarify whether the building’s deletion instruction extends to that copy and how completion is documented.
No specific retention deadline for this project has been established in this review. Avoid importing a duration from another jurisdiction or treating a vendor’s preferred window as a binding condominium requirement. The buyer’s question is whether the proposed schedule is justified, documented, and reviewed by appropriate counsel.
A cybersecurity framework, breach-response process, and designated data-protection officer remain unverified here, as do penetration-test results, vulnerability assessments, SOC 2 assurance documentation, and ISO 27001 certification. Such evidence may nevertheless be available through private due diligence.
Ask what independent security assessment can be shared, when it was completed, and which systems it covers. A vendor credential is not confirmation that every building integration has been assessed. Where technical details are sensitive, request a suitably limited summary rather than unrestricted disclosure.
Then test accountability with practical questions: Who receives a security alert? Who can disable a compromised credential? Who coordinates with vendors and residents? Ask about administrator authentication, software updates, backup recovery, and staff training as verification topics-not presumed features or universal legal obligations.
If a medical-care membership or on-site service is presented as an ownership benefit, verify its scope and provider separately. The offer of an amenity alone would not establish that medical information is shared with building management or connected to entry records.
Ask whether provider information would be segregated from building-access and resident-management data. Request an explanation of what information, if any, would pass between the provider, concierge, management, and service vendors. Distinguish administrative coordination from clinical information, and ask how any permissions would be presented and withdrawn.
If the wider search includes The Well Coconut Grove, carry the same separation questions into that Coconut Grove inquiry without assuming equivalent services or data practices. The purchasing principle remains the same: evaluate an amenity and its information boundaries separately.
Ask Florida condominium counsel to distinguish records the association must maintain from information that may be withheld from owner inspection. Have counsel assess requests for access records rather than assume every retained record is open to every owner.
Request advice on whether Florida’s Information Protection Act applies to the entities and information involved, and what protection and notification duties follow. Ask who would evaluate an incident and coordinate any applicable notifications.
Florida’s Digital Bill of Rights should also be a coverage question for counsel, not an assumed guarantee. Ask counsel to assess statutory thresholds, entity roles, data practices, and exemptions before attributing retention or resident-rights obligations to the association or its vendors. Separate any applicable legal requirements from additional protections a buyer would prefer to see in writing.
Organize the response into four parts: system inventory, access permissions, retention schedule, and incident responsibility. Keep unanswered questions distinct from documented concerns, and distinguish current commitments from features still under consideration.
Ask counsel which representations belong in transaction documents and which policies may change later. A reassuring conversation is no substitute for a clearly identified responsible party and a written explanation. The goal is proportionate confidence, not an unrealistic promise of zero risk.
For a discreet perspective on South Florida residential choices, explore MILLION.
If branded residences are on your mind — as a home or as an allocation — we would be glad to share what we are seeing, privately.
Begin a quiet conversationNo. It identifies pre-purchase verification questions, not evidence of a breach, unlawful processing, or inadequate building security.
The access-control vendor, camera platform, resident-app provider, and cloud-hosting location remain unverified in this review. Those details may be available privately.
Biometric entry remains unverified in this review. Buyers should ask which entry methods are selected and what information each collects.
No project-specific retention period has been established in this review. Request a written schedule covering deletion, preservation exceptions, backups, and vendor copies.
Ask who can view, search, export, and disclose records, and whether those actions are logged. Request a procedure for evaluating disclosure requests.
The availability of penetration-test results, vulnerability assessments, SOC 2 assurance documentation, and ISO 27001 certification remains unverified here. Ask what evidence can be shared through private due diligence.
An amenity alone would not establish data sharing. Verify any service offering and ask how provider information would be separated from building records.
Do not assume a blanket entitlement. Ask Florida condominium counsel which records must be maintained and which information may be withheld from owner inspection.
No; ask counsel to assess coverage rather than assume it. The review should address statutory thresholds, entity roles, data practices, and exemptions for the association and relevant vendors.
Request a system inventory, access-permissions matrix, retention schedule, and explanation of incident responsibility. Ask counsel which representations should be reflected in transaction documents.