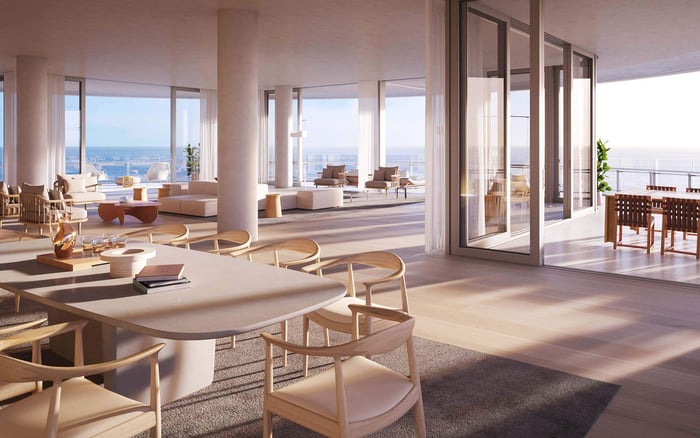
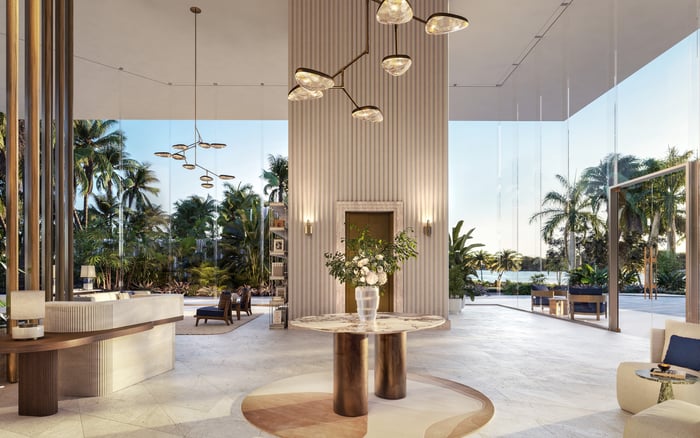
For long-term owners at Eighty Seven Park, privacy diligence should extend beyond staffed security to written rules for administrator access, visitor information, data retention, and emergency continuity.
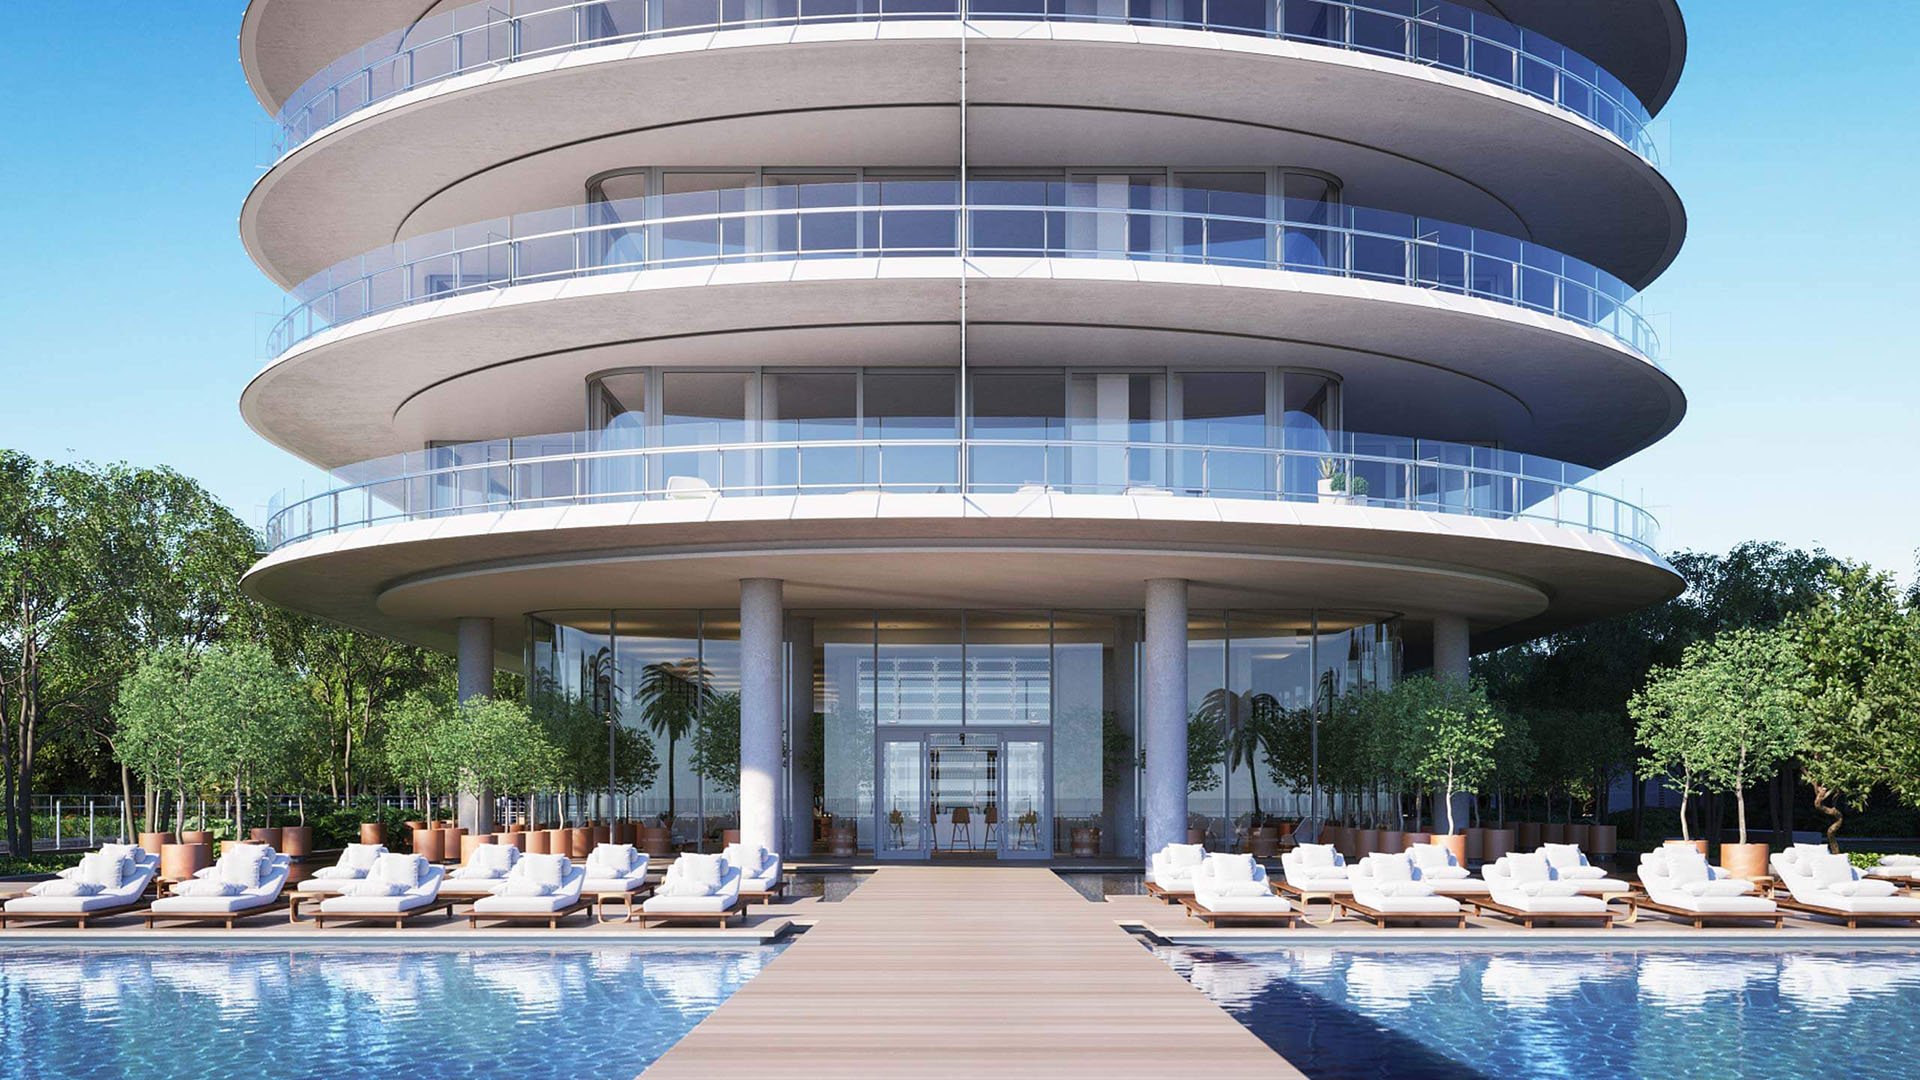
For a long-term owner, discretion extends beyond a quiet arrival. It requires clarity about who can see household information, how access permissions are managed, and what remains on file after a guest, employee, or owner departs. At Eighty Seven Park Surfside, those questions deserve a distinct place in purchase diligence.
The building’s listed address is 8701 Collins Avenue, Miami Beach, FL 33154. Surfside is shorthand in the title, not its listed municipality. Advertised services include 24-hour security, concierge, and valet service. Those descriptions establish a service offering-not cybersecurity capabilities, access-log policies, or resident-data deletion rules.
The building’s cybersecurity architecture, access-control vendor, recorded events, storage location, and retention periods are not established here. That uncertainty is neither evidence of weakness nor assurance of protection. The buyer’s task is to seek current, written answers, not infer technical safeguards from the quality of the arrival experience.
Begin by asking management to distinguish physical security responsibilities from digital administration. Who approves access permissions, who maintains any connected systems, and who can change administrator settings? If outside providers are involved, request a plain-language account of how responsibilities are divided among the association, management, and each vendor.
Ask whether administrator accounts are individually assigned, protected by multifactor authentication, and promptly disabled when personnel leave. Request an explanation of how remote vendor access is approved and withdrawn. These are diligence questions, not descriptions of Eighty Seven Park’s current arrangements.
A nearby comparison illustrates the distinction. Fendi Château Residences Surfside is advertised with security guards, on-site management, card or code access, a secure lobby, and a secure elevator. Those features do not establish its data policies, nor do they describe Eighty Seven Park’s systems. Visible access controls and documented information governance require separate evaluation.
Do not begin with an assumed retention period. Begin with an inventory: which systems, if any, record entry events? Ask management to distinguish an access permission from a record of its use, and both from any visitor register or surveillance footage. Do not presume that any particular record exists.
For each confirmed record category, request details of the information captured, its purpose, and who is authorized to retrieve it. Does an entry identify a person, a credential, a residence, or simply an event? Can information be searched by household? Who may export it, and is retrieval itself recorded?
Apply the same discipline to concierge and valet workflows. Ask what visitor and resident information staff collect, whether it is recorded on paper or electronically, and how it passes between shifts. A useful answer should describe the actual workflow without disclosing sensitive security configurations.
A statement that information is kept securely does not explain how long it remains on file. Request written retention and deletion rules for each category management confirms it holds. Ask what starts the retention period, who approves exceptions, and how deletion is documented.
Storage warrants separate scrutiny. Is information held on building-controlled equipment, by a service provider, or in multiple locations? If copies or backups exist, ask how their retention differs from that of the active system. Request an explanation of the circumstances, if any, in which routine deletion is suspended, with counsel reviewing legal obligations where appropriate.
Long-term ownership also calls for an exit plan. What happens to resident profiles and permissions after a sale? How are former household staff and recurring visitors removed? If a vendor is replaced, who oversees data transfer and deletion? Seek a defined procedure rather than assume that closing or contract termination automatically clears every record.
For an owner who is frequently away, convenience should not depend on unclear authority. Ask how management distinguishes an owner’s instructions from requests made by an assistant, family member, property manager, or service provider. Request the process for granting, limiting, and withdrawing delegated permissions.
Consider a practical walkthrough: a household employee leaves while the owner is abroad. Who receives the instruction to revoke access, how is that instruction authenticated, and how does management confirm completion? The value lies in a repeatable process, not a promise that someone at the desk will remember.
Buyers also considering The Surf Club Four Seasons Surfside can bring the same questions to that review. This is a common diligence framework, not a claim that the properties share vendors, systems, or privacy practices.
In July 2021, following the Champlain Towers South collapse, gas and utilities at Eighty Seven Park had been cut off, and visitor entry was subject to a waiver. That was a historical emergency restriction, not evidence of today’s access policy or digital-security practices.
The relevant ownership question is forward-looking: what written procedures apply when normal operations are interrupted? Ask how resident communications, visitor authorization, and essential access would be managed during a system outage. If temporary records are created, ask who controls them and how they are subsequently retained or deleted. Emergency flexibility should come with defined authority and a documented return to normal procedures.
Organize the request to management around five subjects: current resident-data rules; any access-record inventory and retention schedule; vendor responsibilities; administrator-access safeguards; and incident-response and notification procedures. Where detailed technical material is sensitive, ask whether a qualified adviser can review an appropriate summary through a controlled process.
For incident procedures, ask who receives an initial concern, who decides whether resident information may be affected, and how owners would be contacted. Seek clarity about responsibility rather than invent a notification deadline or assume one applies to every event.
Then examine the ownership horizon. Ask what the budget provides for system maintenance, software support, equipment replacement, staff training, and periodic review. If contracts change or equipment reaches the end of support, who is accountable for continuity? These questions connect daily privacy expectations to the association’s longer-term management and funding decisions.
The strongest answer is not necessarily the most technical. It is a coherent explanation of what information is collected, why it is needed, who can use it, and when it is removed-supported by current documents and clear accountability.
For Eighty Seven Park buyers, advertised service and written governance should be evaluated side by side. Neither an elegant lobby nor an unanswered question should substitute for evidence. Before committing, identify which answers are documented, which need professional review, and which remain unresolved.
For a considered approach to South Florida luxury ownership, explore MILLION.
If branded residences are on your mind — as a home or as an allocation — we would be glad to share what we are seeing, privately.
Begin a quiet conversationIts listed address is 8701 Collins Avenue, Miami Beach, FL 33154. Surfside is shorthand in the article title, not its listed municipality.
No. Staffed security is a service description and does not establish digital safeguards, administrator controls, or resident-data policies.
The existence and scope of access-control logs are not established here. Ask management which systems, if any, record entry events and what information they capture.
A building-specific retention period is not established here. Request a written schedule for each confirmed category of resident and visitor information.
Ask whether accounts are individually assigned, protected by multifactor authentication, and disabled when personnel leave. Also request the procedure for approving and withdrawing remote vendor access.
Both services are advertised at Eighty Seven Park. Buyers should ask what information staff collect, how it moves between shifts, and who may retrieve it.
Ask management how resident profiles and permissions are closed and how retained information is handled. Do not assume a sale automatically deletes every record.
No. The waiver requirement was a historical emergency restriction following the Champlain Towers South collapse, not evidence of current access policy.
No. Fendi Château’s advertised security and access features apply to that property and do not establish Eighty Seven Park’s systems or either building’s data policies.
Ask how the budget addresses system maintenance, software support, equipment replacement, staff training, and periodic review. Request clarity about responsibility when vendors change or support ends.