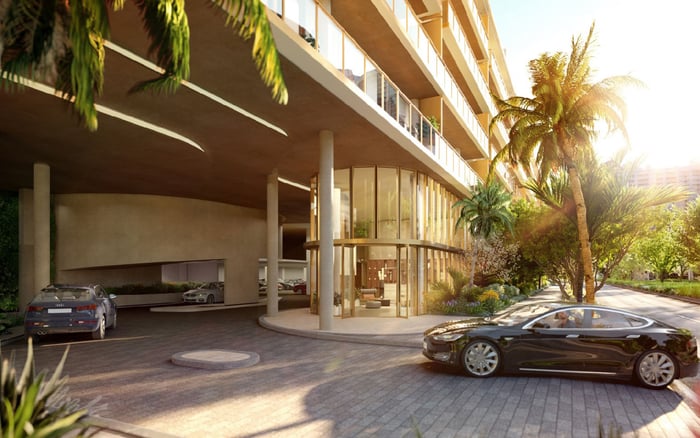
2200 Brickell’s advertised physical-security features are a starting point, not a cybersecurity assessment. A practical buyer review should address access permissions, administrator controls, resident-data retention, vendor responsibilities, and the credential handover at closing.
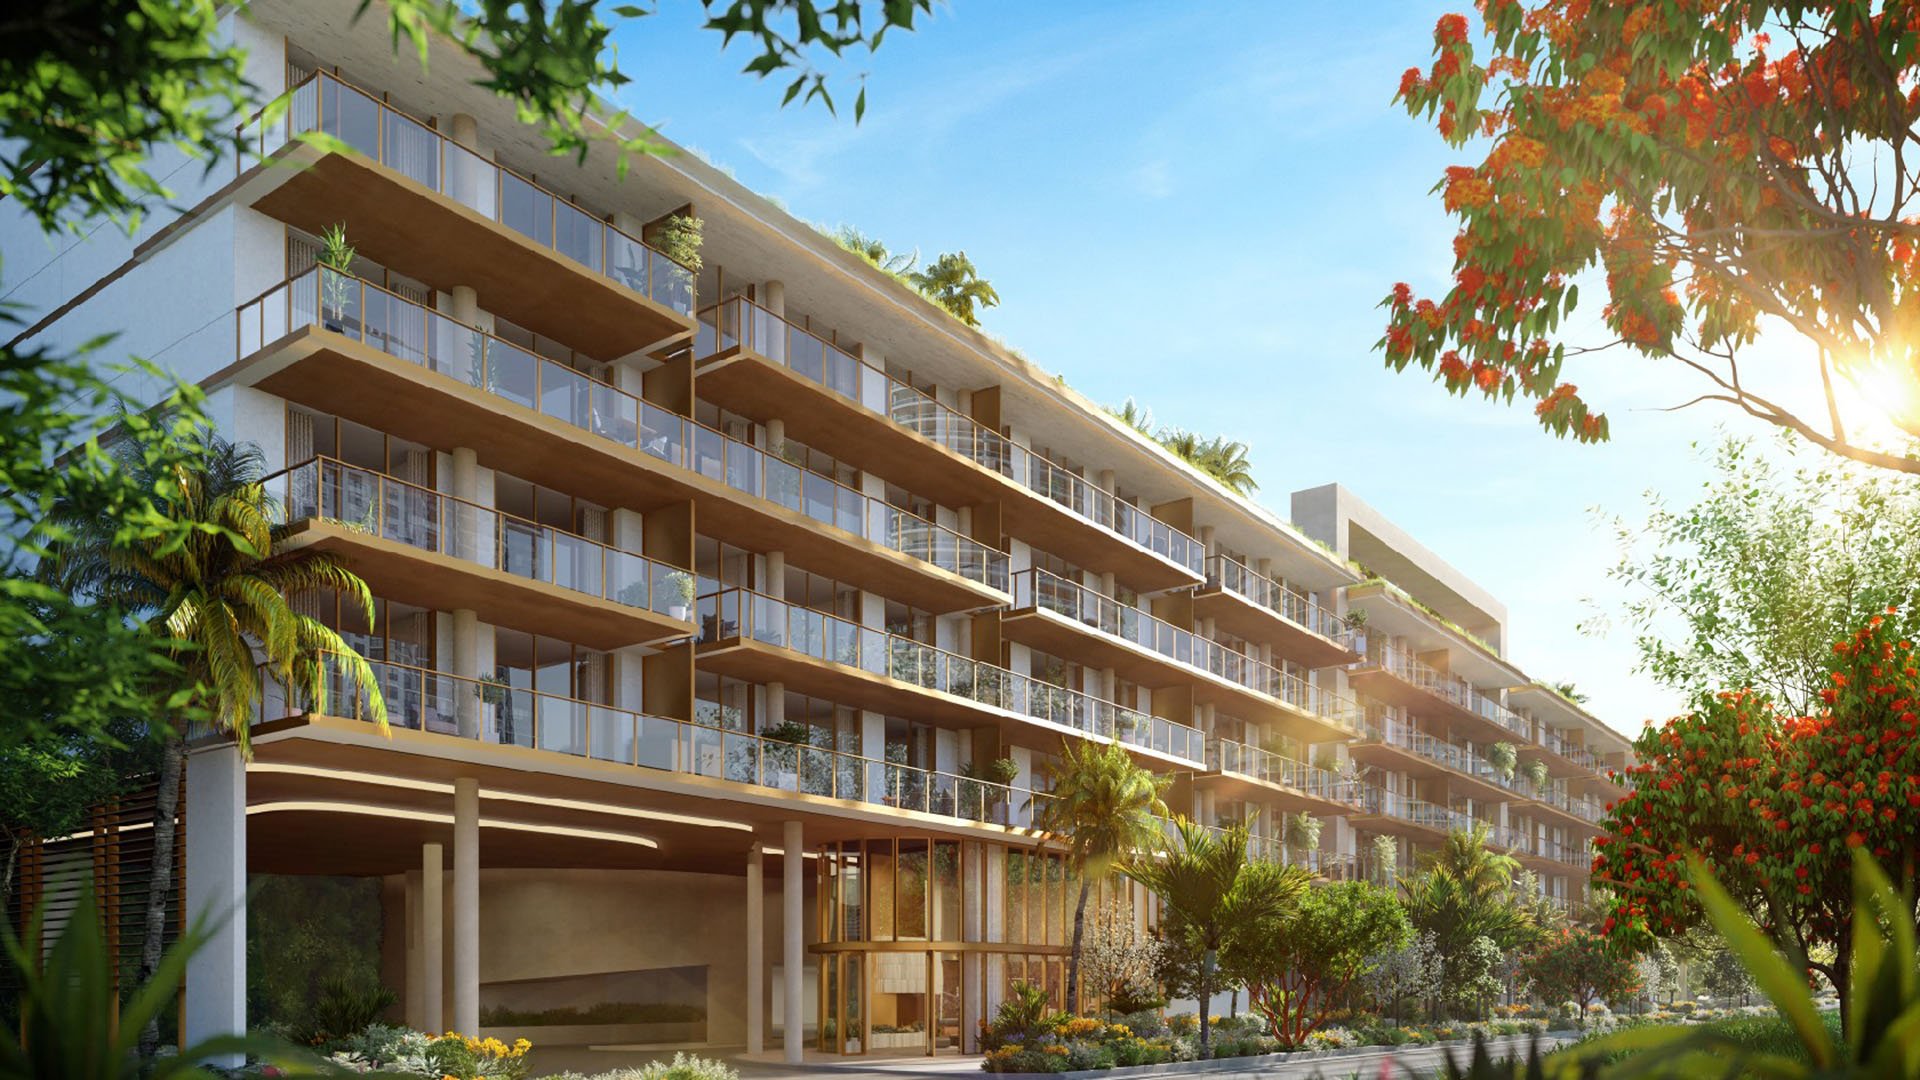
For a luxury homeowner, discretion extends beyond the lobby. It includes who can retrieve an arrival history, how guest information is handled, and whether former occupants retain digital access after a sale. At 2200 Brickell, located at 2200 Brickell Avenue, Miami, FL 33129, those questions belong alongside the conventional ownership review.
The advertised features describe layered physical security. They do not establish cybersecurity maturity or resident-data governance. A buyer should neither assume sophisticated controls are in place nor treat undisclosed details as evidence of failure. The objective is practical: obtain written answers about permissions, retention, and accountability before making a contractual commitment.
Advertised features for residence GV02 include key/card building entry, common-building security, and an attended lobby. For residence #422, they include doorman service, security-guard coverage, secured elevators, and secured garage or parking access. Smoke detection and fire alarms also appear among its security features.
These are useful starting points, not independently verified operating conditions. Secured elevators do not establish floor-specific permissions. Secured parking does not identify the credential technology, whether entry events are recorded, or who may inspect those records.
Ask management to explain the intended resident journey from garage to elevator to residence, including visitor access. Keep life-safety features in their proper category: smoke detection and fire alarms do not answer questions about digital account protection, vendor access, or the handling of personal information.
A useful first document would identify each applicable access-control, camera, concierge, valet, package-management, and resident-app system, along with its vendor and responsible administrator. This is a proposed diligence request-not an inventory of systems confirmed at 2200 Brickell.
For each system, ask who administers it, who supports it remotely, and whether resident information is stored locally or in a vendor’s cloud environment. Confirm whether administrative accounts use multifactor authentication and whether a recent cybersecurity assessment is available for review. A summary of findings and remediation status may be more appropriate than sensitive technical detail.
Buyers also considering Una Residences Brickell can use the same questionnaire without presuming the properties share vendors, controls, or policies. Comparisons should rest on documented responsibilities, not the language used to describe a secure arrival experience.
An access credential and its associated history raise different questions. One concerns permission to enter; the other concerns the information that may remain afterward. At 2200 Brickell, the advertised access features do not establish the contents, retention period, or inspection rules for any access logs.
Request a plain-language explanation of whether events are logged and, if so, which fields are captured. Ask whether a record identifies a credential, person, location, or time, and how temporary guest permissions are distinguished from resident permissions. These are questions to resolve, not verified characteristics of the building.
Then address oversight: who may search or export records, what approval is required, and whether administrator activity is itself recorded. A buyer needs the rules governing access, not another resident’s movement history. Sample policy language or a redacted demonstration can clarify that distinction without exposing private information.
A website-cookie disclosure should not be treated as a comprehensive retention policy for building-access records, surveillance footage, resident profiles, or concierge data.
No building-specific retention schedule is established here. Do not substitute an assumed number of days or years. Request separate schedules for each applicable category: access logs, footage, guest records, vehicle information, amenity bookings, and resident identity data.
Each schedule should explain when retention begins, when routine deletion occurs, and who authorizes exceptions. Ask how an incident or dispute changes routine deletion and how evidence-preservation instructions reach vendors. Clarify what happens to backups as well as active records; deletion from one system should not be assumed to remove every copy.
Second-home buyers should also ask how periods of absence affect guest permissions and account maintenance. Seek a documented procedure, not a general assurance that information is kept only as long as necessary.
Request the privacy and service terms governing any vendors that handle resident information. Focus on storage, sharing, analytics, marketing, and AI-training uses. Ask which uses are necessary to deliver a service, which are optional, and who can approve changes. None of these uses should be presumed to occur at 2200 Brickell.
The incident-response review should identify who receives an alert, who can suspend compromised credentials, and who coordinates with the affected vendor. Obtain the applicable breach-notification and evidence-preservation procedures, including how they address vendor-held backups. Have counsel review the responsibilities and notification language rather than infer protections from a concierge offering.
For a purchaser weighing The Residences at 1428 Brickell as another option, these requests provide a consistent comparison framework. They imply no conclusion about either property’s cybersecurity practices.
Florida condominium law requires associations to maintain official records and governs unit-owner access to them. That framework should not be treated as a verified retention rule for every security-system dataset.
The condominium-records provisions restrict owner inspection of sensitive identifiers, including Social Security, driver-license, and credit-card numbers. Certain contact details, emergency-contact information, and other personal identifying information are also protected, subject to statutory exceptions.
An ownership review should distinguish requests for governance documents from requests for personal records. Seek policies, applicable contract terms, and clear explanations of responsibilities. Have condominium counsel assess which requested materials are inspectable and what redactions or exceptions apply. Ownership does not confer unrestricted access to neighbors’ information.
Resale purchasers should request a written credential handover plan. Identify which accounts or credentials transfer, which must be recreated, and who confirms that the outgoing owner’s and former occupants’ permissions have ended. Include any applicable guest, household staff, vehicle, and vendor permissions in that review.
The closing checklist should also name the contact for lost credentials, account corrections, and unresolved privacy questions. Written confirmation is more useful than assuming a change in ownership automatically updates every connected service.
The conclusion is measured: 2200 Brickell’s advertised physical-security features merit consideration, while cybersecurity and resident-data practices require separate confirmation. The ownership decision should reflect both the arrival experience and the documented rules governing information after arrival.
For a discreet perspective on your South Florida ownership search, connect with MILLION.
If branded residences are on your mind — as a home or as an allocation — we would be glad to share what we are seeing, privately.
Begin a quiet conversation2200 Brickell is located at 2200 Brickell Avenue, Miami, FL 33129, in Miami’s Brickell area.
Advertised features include key/card entry, an attended lobby, doorman service, security-guard coverage, secured elevators, and secured parking. These are not independently verified operating conditions.
Secured elevators are advertised, but floor-specific permissions are not established. Buyers should request a written explanation of elevator access rules.
No. Physical-security features do not establish cybersecurity maturity, and undisclosed digital controls should be treated as unknown rather than absent.
No building-specific retention schedule is established here. Buyers should request separate retention and deletion schedules for each applicable dataset.
No. Buyers should request policies specifically covering building-access records, surveillance footage, resident profiles, and any concierge data.
Ask who has administrative access, whether those accounts use multifactor authentication, and how permissions are revoked. Request any available recent cybersecurity assessment for review.
No. Florida’s condominium-records provisions restrict inspection of sensitive identifiers and certain other personal information, subject to statutory exceptions.
Review terms covering storage, sharing, analytics, marketing, and AI-training uses, along with incident-response and evidence-preservation responsibilities. These are diligence topics, not confirmed vendor practices at 2200 Brickell.
Buyers should request a written plan identifying credentials that transfer or must be recreated and confirming removal of outgoing occupants’ permissions. The plan should identify who is responsible for completing those steps.