An owner-focused review of what keyless entry establishes at The Residences at Mandarin Oriental, Miami, and the alternatives, consent safeguards, and fallback procedures worth requesting before biometric enrollment.
At The Residences at Mandarin Oriental, Miami, the owner-operations question is not simply how elegantly a door opens. It is whether access remains discreet, dependable, and available without requiring an owner to surrender biometric information. A strong access policy should make convenience optional and continuity fundamental.
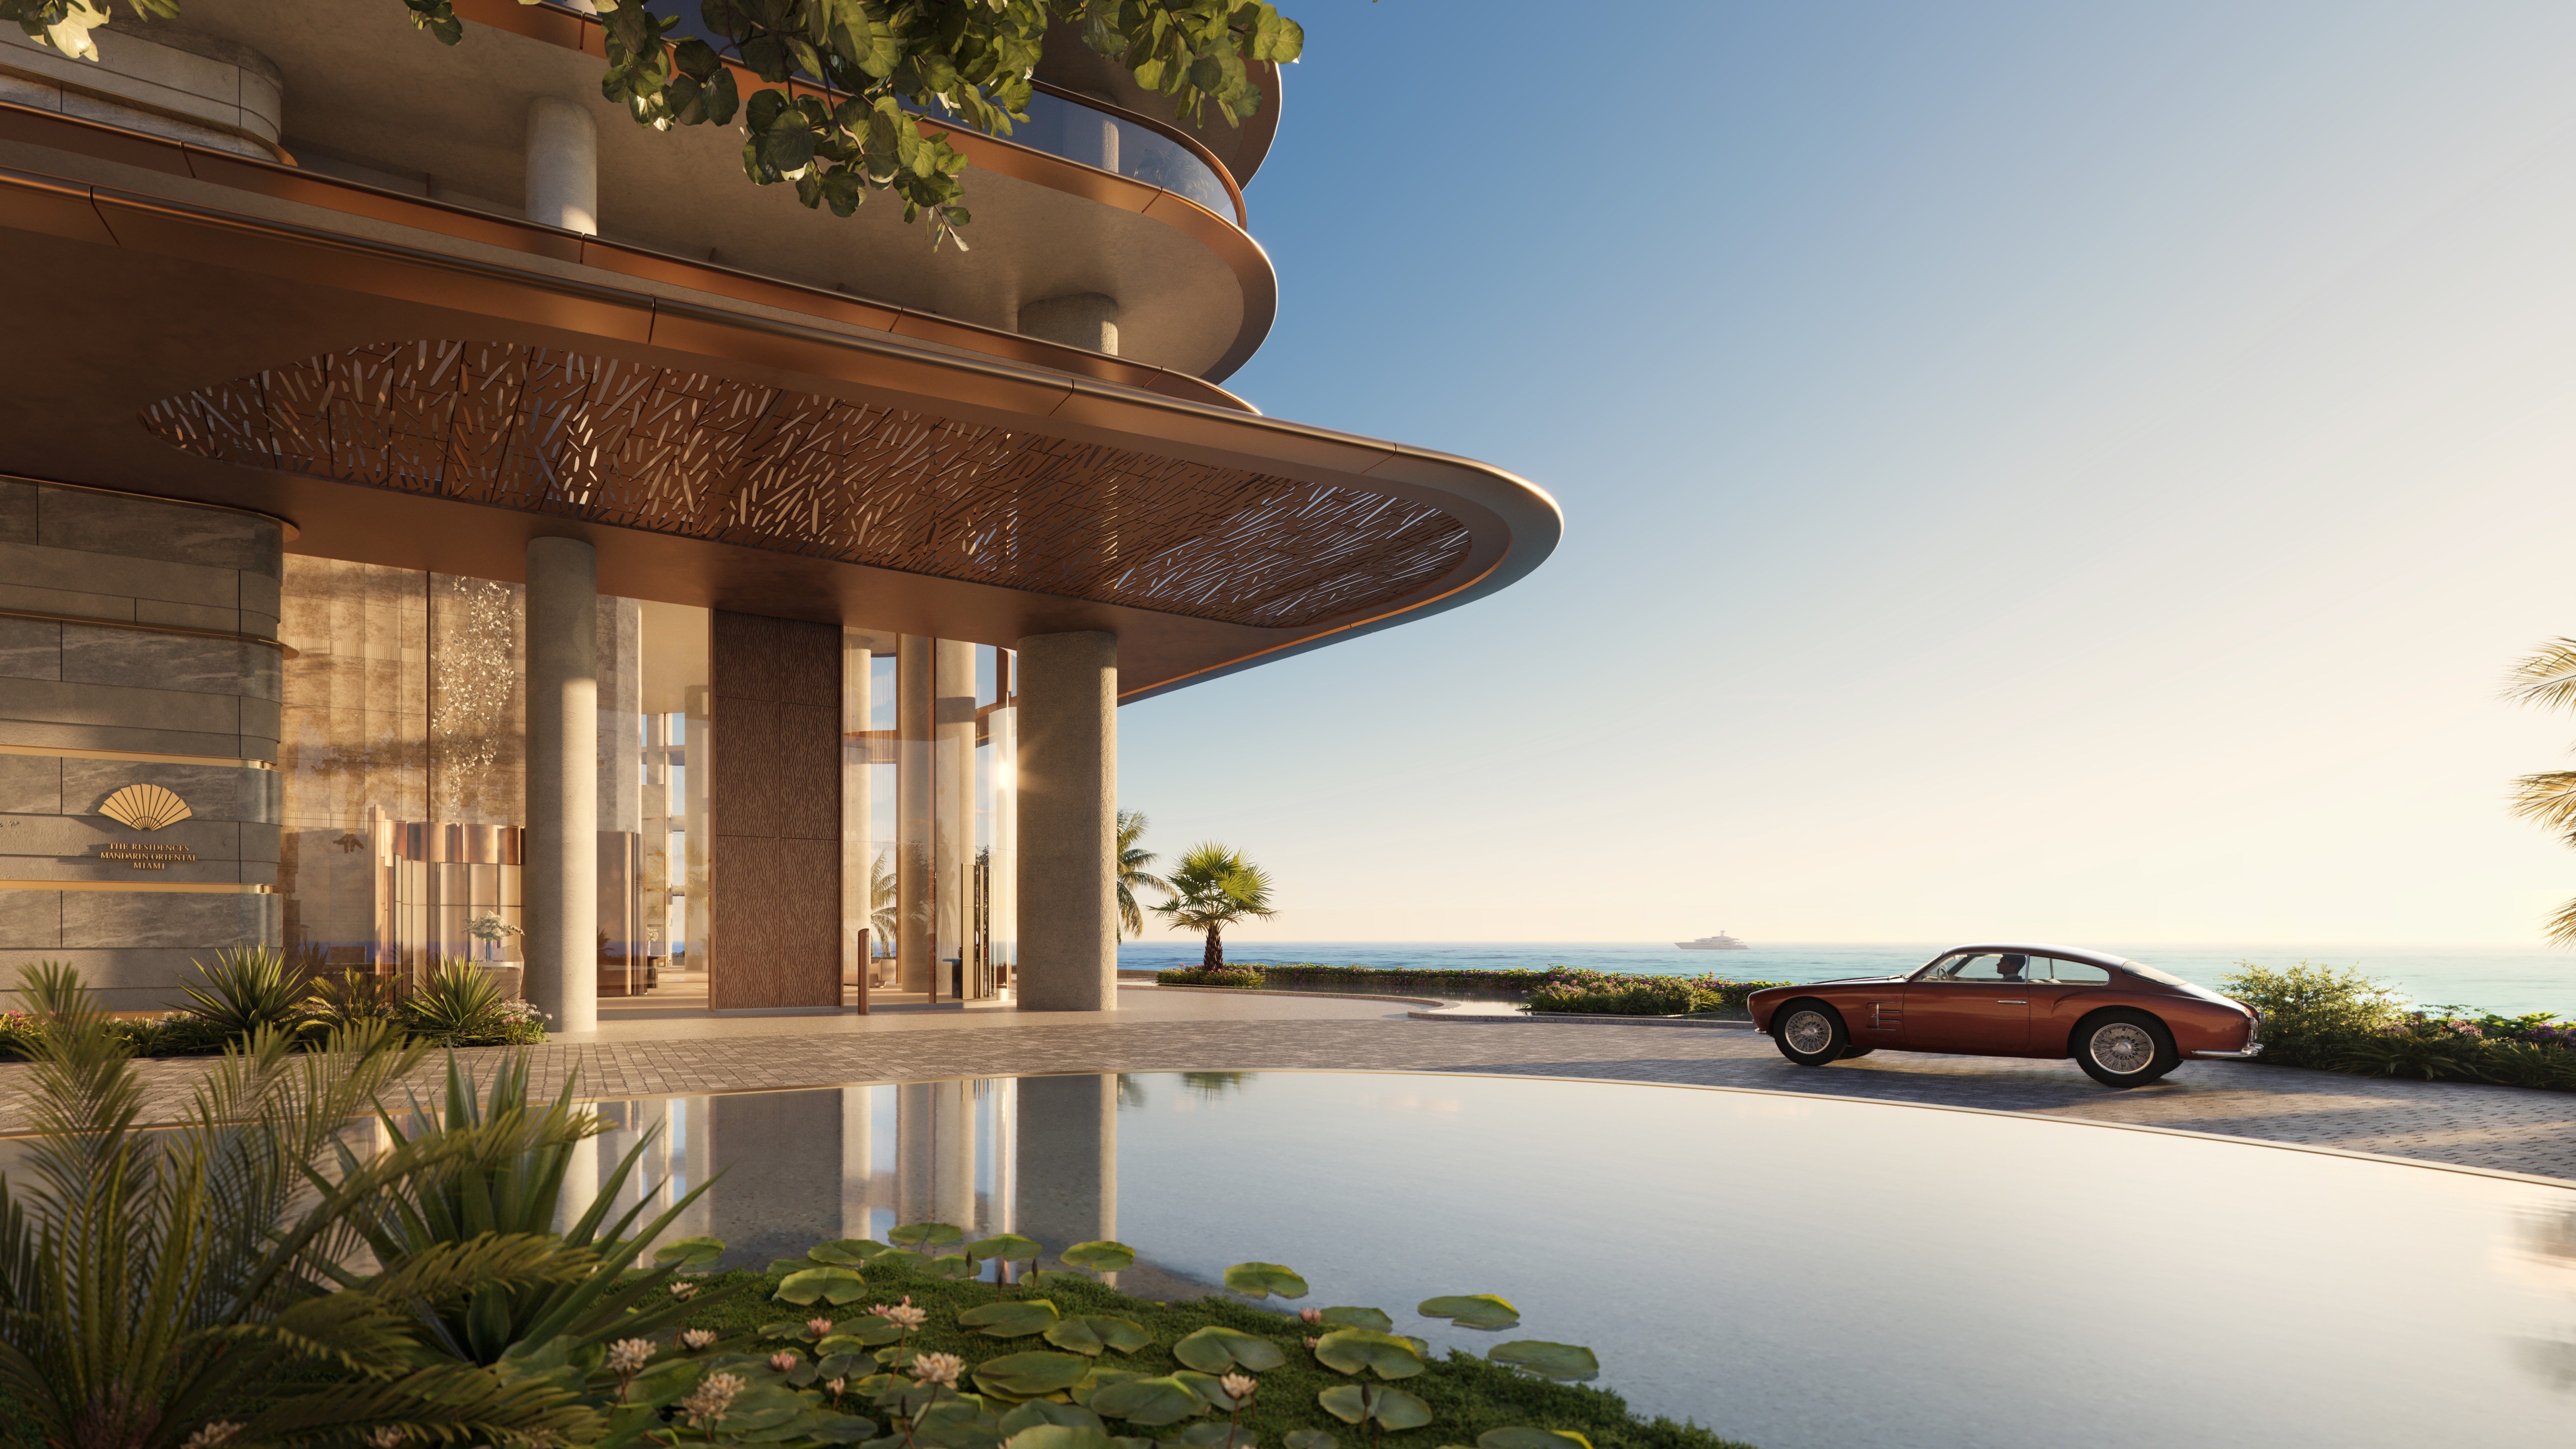
The project address is 750 Claughton Island Drive, Miami, FL 33131. Residence features describe a double-door main entrance with keyless entry, alongside gated access with dedicated 24-hour security. North Tower features separately include 24-hour security, a dedicated residential lobby and elevators, and keyless entrance. These descriptions should remain distinct, not be combined into a single technical specification.
Keyless entry does not establish biometric access. It does not specify whether the credential is a phone, card, fob, keypad code, or biometric identifier. Biometric deployment, mandatory enrollment, a biometric-consent form, and actual fallback procedures are not publicly established in the information available for this review. The recommendations below are therefore an owner due-diligence framework, not a description of adopted property policy.
For an owner, the meaningful distinction is between a feature and an operating commitment. A reference to keyless entry describes an experience; it does not explain who issues credentials, who can suspend them, or what happens when a reader stops responding.
Owners should request a written access schedule that separates the gated perimeter, residential lobby, elevators, shared spaces, and residence entrance. For each access point, ask which credentials are accepted, who administers permissions, and how an authorized resident enters during a failure. Dedicated security is a stated feature, but its presence alone does not establish an emergency-entry protocol.
The same distinction applies to a Brickell comparison involving Cipriani Residences Brickell: assess written operating commitments rather than infer access technology from a residential brand. Do not assume equivalent credential systems or privacy policies across properties.
If biometrics are proposed, the preferred approach for owners is optional enrollment alongside a practical non-biometric credential. Mobile credentials and encrypted cards or fobs are alternatives to request, not confirmed amenities at this property.
Assess the alternative for everyday usability. Owners should ask whether it provides access to the same authorized destinations, works during the same access hours, and requires additional staff intervention. An option that routinely delays entry deserves scrutiny, even if it is technically available.
Mobile access should not be the only fallback considered. Ask how an owner enters with a lost phone or depleted battery, and whether a separately issued card or fob would remain usable. For a lost physical credential, request the replacement and revocation process.
The operating proposal should also distinguish owners, household members, guests, and service personnel. Request defined permissions and expiration rules for each category rather than presume a single credential policy can accommodate every arrival discreetly.
If biometric enrollment is offered, the recommended procedure is to present a separate consent document before collection. It should identify the biometric modality, the specific access purpose, the provider, and the entity responsible for administering the information. This is an operational recommendation, not an established property requirement or a universal statement of Florida law.
Owners should request plain-language answers about what is collected, where it is held, who can access it, whether it is shared, and how long it is retained. The document should distinguish withdrawal from deletion: stopping biometric entry and removing retained data are separate matters that require explicit treatment.
The non-biometric alternative should be explained at the same time, including how to obtain it. A proposed withdrawal procedure should allow the replacement credential to be activated before biometric access is disabled, subject to appropriate identity checks.
General public-facing privacy information does not itself establish the collection, retention, or deletion rules for a residential access system. Owners should request access-specific notice and consent terms rather than treat general privacy language as sufficient operational assurance.
A fallback should be a documented procedure, not an improvised courtesy. The proposed policy should name authorized credential issuers, define accessible areas, set expiration rules where appropriate, and explain access logging and revocation.
Owners should request procedures covering four situations:
Reader failure: Identify the authorized alternative when the usual access point cannot recognize a credential.
Power or network interruption: Specify which access functions remain available and when security-controlled assistance takes over.
Lost device or credential: Explain identity verification, cancellation of the missing credential, and temporary or replacement issuance.
Consent withdrawal: Describe the transition to non-biometric access without leaving an authorized owner dependent on an unresolved enrollment dispute.
For each situation, ask who is responsible, how to reach assistance, and what record is retained. Temporary access should have a defined end point and review process. These controls are recommendations, not confirmation of existing procedures.
Florida's Digital Bill of Rights classifies biometric data processed to uniquely identify an individual as sensitive data. Its application nevertheless depends on statutory coverage, the processing entity, and applicable exemptions. Owners should not assume every condominium association falls within its scope.
Biometric-equipment installation and related common-area changes may implicate condominium-law and governing-document approvals. Making biometric submission the sole condition of entry may also generate disputes over owners' access rights. Current advice on Florida condominium and privacy law should precede deployment or a material policy change.
Before accepting any biometric proposal, request the credential specification, access-area schedule, enrollment terms, access-specific privacy notice, fallback procedure, and applicable approval record. Ask which documents are final, who may revise them, and how owners will receive notice of changes.
For buyers also considering St. Regis® Residences Brickell, these questions provide a consistent comparison framework without implying shared technology or governance. Evaluate each property's commitments independently.
At Mandarin Oriental, the decisive standard is straightforward: establish what keyless means, preserve a workable choice if biometrics are offered, and document how authorized access continues when the preferred credential is unavailable. That operational detail allows privacy and effortless arrival to coexist.
For a discreet perspective on South Florida residential ownership, explore MILLION.
If branded residences are on your mind — as a home or as an allocation — we would be glad to share what we are seeing, privately.
Begin a quiet conversationBiometric deployment is not publicly established in the available project information. Keyless entry alone does not confirm fingerprint, facial, or other biometric recognition.
Residence features describe a double-door main entrance with keyless entry, alongside gated access with dedicated 24-hour security. North Tower features separately describe security, a dedicated residential lobby and elevators, and keyless entrance.
The listed address is 750 Claughton Island Drive, Miami, FL 33131.
Owners should ask about mobile credentials and encrypted cards or fobs, together with security-controlled emergency access. These are recommended alternatives, not confirmed property amenities.
It should identify the biometric modality, purpose, provider, responsible entity, retention, sharing, and withdrawal procedure. It should also explain the non-biometric alternative before enrollment.
No. General website privacy information does not itself establish how a residential access system would collect, retain, or delete biometric data.
A recommended procedure would activate an authorized non-biometric replacement before disabling biometric access. Withdrawal and data deletion should be addressed separately in writing.
Owners should request procedures for reader failures, power or network interruptions, lost devices or credentials, and consent withdrawal. Each should identify responsible personnel and issuance, logging, and revocation controls.
Coverage should not be assumed. Applicability depends on statutory criteria, the processing entity, and exemptions, requiring current legal review.
Biometric equipment and related common-area changes may implicate condominium law and governing-document approval requirements. Making biometrics the sole route to entry may also raise access-rights disputes.