An owner-focused review of Onda Bay Harbor’s advertised security services and the operational questions that matter beyond them, from credential controls and protected access logs to resident-data retention and Florida legal obligations.
In a luxury residence, discretion should extend beyond arrival to the information a building collects. For owners at Onda Bay Harbor, an effective operational review begins by separating advertised services from the controls governing credentials, surveillance footage, and resident information.
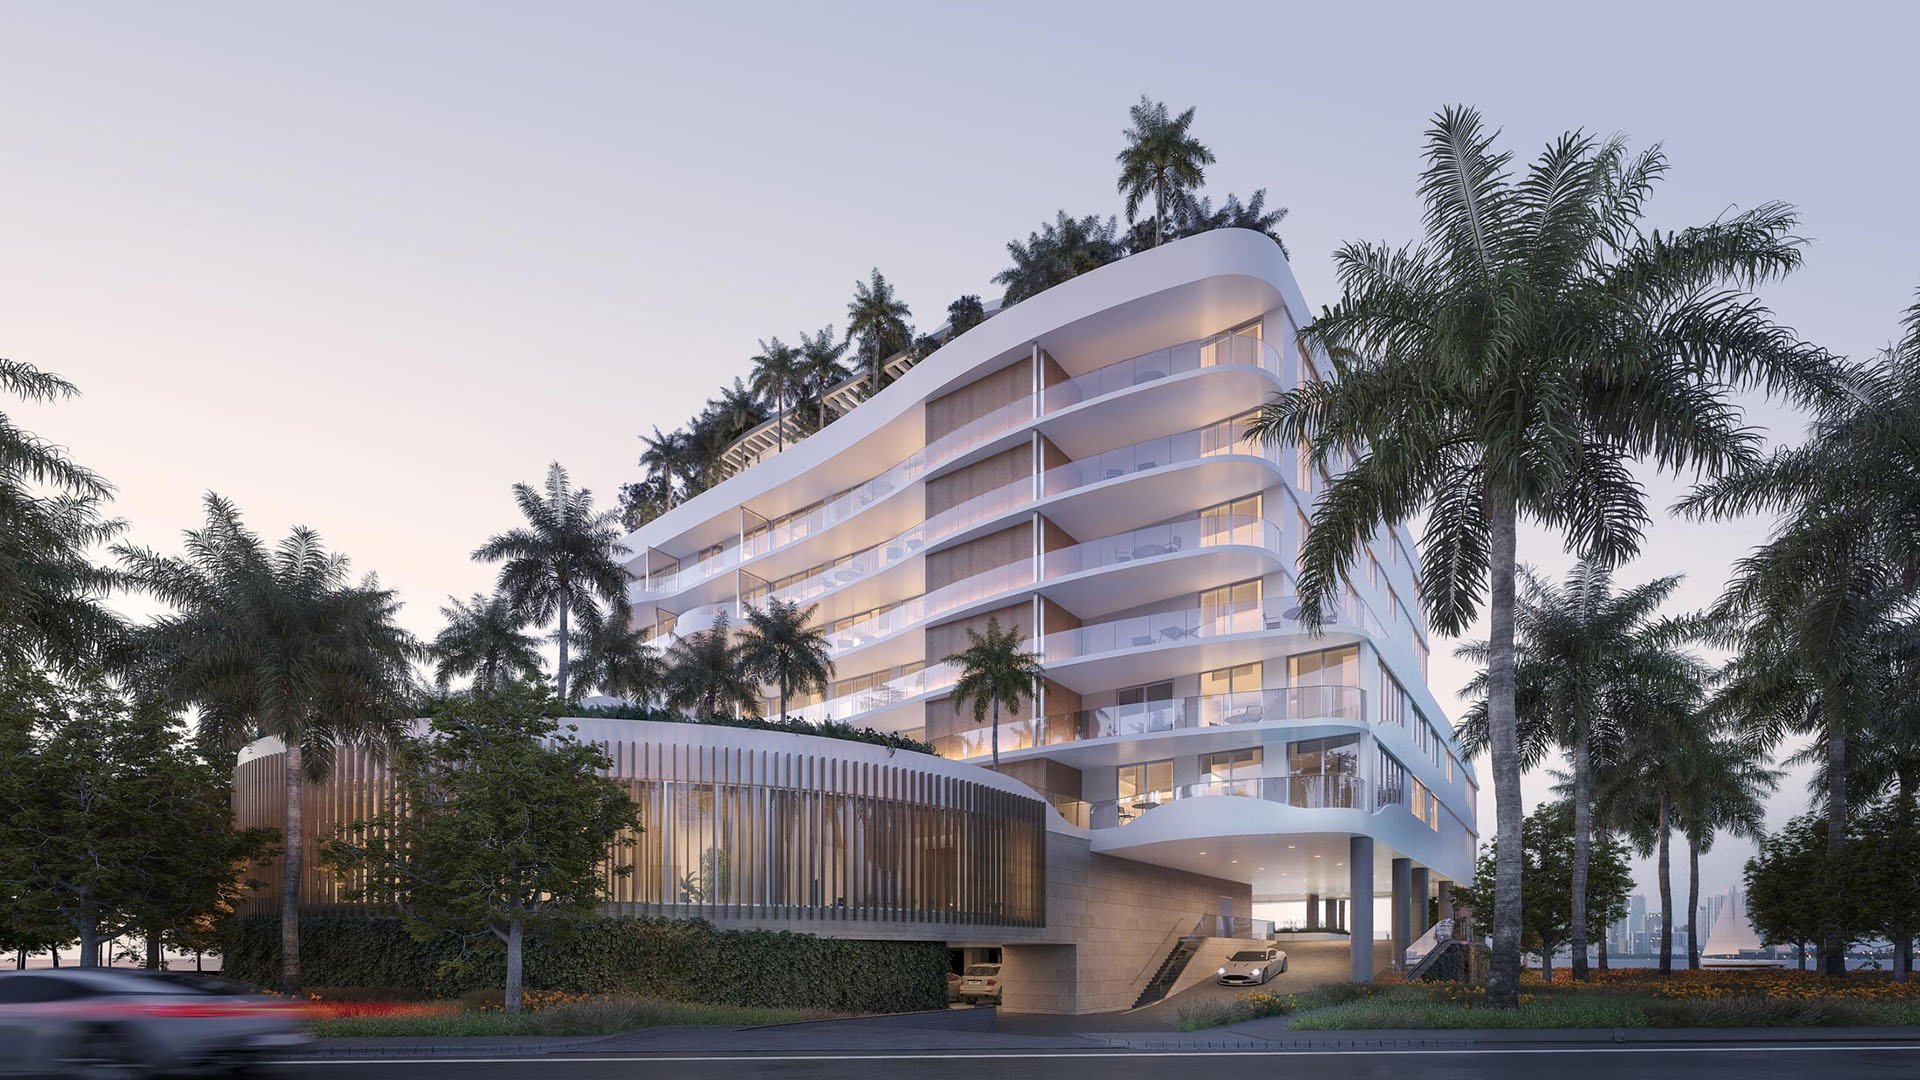
Onda is located at 1135 103rd Street, Bay Harbor Islands, FL 33154, and its developers are CMC Group and Morabito Properties. Advertised services include 24-hour security video surveillance and 24-hour valet service. Those offerings do not establish the building’s cybersecurity program, credential-management procedures, surveillance-retention periods, or incident-response process.
That distinction is not a finding of weakness. It defines what owners should verify with management. The objective is documented accountability: who can enter, who can examine the records, how long information remains available, and what happens when authorization ends.
Begin with an access-control policy, a system and vendor inventory, a category-specific retention schedule, a resident privacy notice, and an incident-response plan. Together, these should explain how information is managed in the course of daily service.
The inventory should identify which systems handle building access, surveillance, and resident information, and which vendors administer them. The privacy notice should explain collection and use; the retention schedule should address preservation and disposal. Ask management who is responsible for each document and for keeping procedures current.
For buyers also considering Bay Harbor Towers, the same document request provides a consistent basis for comparison. It does not presume that either property uses a particular technology or follows identical policies.
An owner-facing explanation need not expose sensitive system configurations. Request policy summaries and appropriately redacted evidence, not unrestricted access to other residents’ records.
A credential review should cover issuance, permission changes, recurring review, and removal. Ask whether administrative users have individual identities, privileges are limited by role, and multifactor authentication protects administrative access. These are review benchmarks, not confirmed Onda features or automatically binding condominium requirements.
Temporary accounts should expire automatically and carry only the permissions needed for their authorized purpose. Management should also explain how it handles a departing employee, an ended vendor assignment, or a compromised credential. Prompt removal matters as much as careful initial approval.
Second-home owners should ask how temporary authorization is documented when they are away. The question is not simply whether access can be arranged, but how its scope and expiration are controlled.
Recurring access reviews complete the picture. Ask who checks that active credentials still serve a legitimate purpose and how exceptions are resolved. A policy is more useful when responsibility for applying it is clear.
Useful access records should identify the person or credential involved, the event time, the access point, and the outcome. Denied and successful entries are distinct events; a review should establish whether the records preserve that distinction.
Log management covers the full lifecycle of records, from generation and transmission through storage, access, and disposal. Ask whether timestamps are synchronized, administrative permissions are restricted, and records are protected against unauthorized modification or deletion. Without those safeguards, a sequence of events becomes harder to interpret.
For retained logs, ask vendors about tamper-resistant measures, including immutable or write-once storage and stronger deletion controls. These are safeguards to evaluate, not evidence of Onda’s current configuration.
Clarify who may retrieve records and authorize disclosure. An owner’s interest in accountability does not call for unrestricted visibility into neighbors’ movements. The review should test both the records’ investigative value and the limits on access.
Network segmentation is another appropriate benchmark: security-sensitive systems should be separated from less-trusted networks. Onda’s actual network configuration remains unverified, so owners should request an explanation from management or vendors rather than assume that separation exists.
Administrative access deserves similar scrutiny. Ask whether vendor personnel use individually identifiable accounts, whether their privileges match their responsibilities, and how access ends when an assignment concludes. Confirm who reviews those permissions.
A buyer considering The Well Bay Harbor Islands can apply the same questions without assuming shared infrastructure or operating practices. Compare the clarity of documented controls, not the prominence of a project’s branding.
No Onda-specific surveillance or access-log retention duration is established here. Owners should not treat a suggested period, such as 90 days or one year, as building policy or Florida law.
Instead, request separate treatment for operational logs, visitor records, identification documents, incident evidence, and statutory records. A retention schedule should define each category’s purpose and align its duration with investigative, regulatory, and organizational needs. One period need not fit every category.
Disposal belongs in the same discussion. Ask how information is removed when no longer required and how applicable holds or continuing legal obligations suspend routine deletion. Keeping everything indefinitely is not a substitute for a defined policy.
This approach also offers a basis for comparison with Rivage Bal Harbour. For buyers considering Bal Harbour, documented retention rules deserve attention alongside the more visible elements of residential service.
Florida Statutes §501.171 requires covered entities to take reasonable measures to protect electronic data containing personal information and establishes notification duties for qualifying breaches. Applying it requires assessing the actual information collected against the statute’s definitions.
Ordinary contact information should not automatically be equated with covered identification, financial, biometric, or account-access information. Ask counsel to assess the relevant data categories and obligations rather than classify every resident record identically.
A separate January 1, 2026 digital-records requirement concerns condominium associations with 25 or more units under §718.111(12)(g). Counsel should confirm applicability and implementation requirements for the association. That requirement should not be interpreted as a universal surveillance-retention mandate or permission to make sensitive access records broadly available.
Finally, request a documented incident-response plan identifying who coordinates management, technology vendors, and counsel. Ask how potentially compromised credentials are addressed, relevant evidence is preserved, and applicable notification obligations are evaluated. Onda’s advertised services do not establish its incident-response process.
The desired outcome is straightforward: named responsibilities, controlled access, reliable records, and deliberate disposal. For an owner, those answers make privacy and security assessable rather than merely reassuring.
For a discreet perspective on South Florida ownership and residential due diligence, explore MILLION.
If branded residences are on your mind — as a home or as an allocation — we would be glad to share what we are seeing, privately.
Begin a quiet conversationOnda Bay Harbor is at 1135 103rd Street, Bay Harbor Islands, FL 33154. Its identified developers are CMC Group and Morabito Properties.
Advertised services include 24-hour security video surveillance and 24-hour valet service. These offerings do not establish the building’s cybersecurity or resident-data policies.
Request the access-control policy, system and vendor inventory, category-specific retention schedule, resident privacy notice, and incident-response plan.
Ask whether records identify the person or credential, event time, access point, and outcome. Synchronized timestamps and safeguards against unauthorized changes are also important review benchmarks.
Individual identification, role-limited privileges, and multifactor authentication are appropriate benchmarks to verify. Their implementation at Onda is not established here.
Temporary accounts should expire automatically and carry only necessary permissions. Procedures should also address prompt removal when authorization ends or credentials are compromised.
No Onda-specific retention duration is established here. Ask management for its written schedule rather than assume a particular period.
A review should distinguish operational logs, visitor records, identification documents, incident evidence, and statutory records. Disposal must also account for applicable holds and continuing legal obligations.
Applicability depends on the statute’s definitions and the actual data collected. Ordinary contact information should not automatically be treated as covered identification, financial, biometric, or account-access information.
The January 1, 2026 requirement under §718.111(12)(g) concerns digital records for condominium associations with 25 or more units, not a universal surveillance-retention period. Counsel should confirm applicability and implementation requirements.