A buyer-focused guide to evaluating resident-data governance at Alba West Palm Beach, from access permissions and retention schedules to records inspection, incident preservation, and secure disposal.
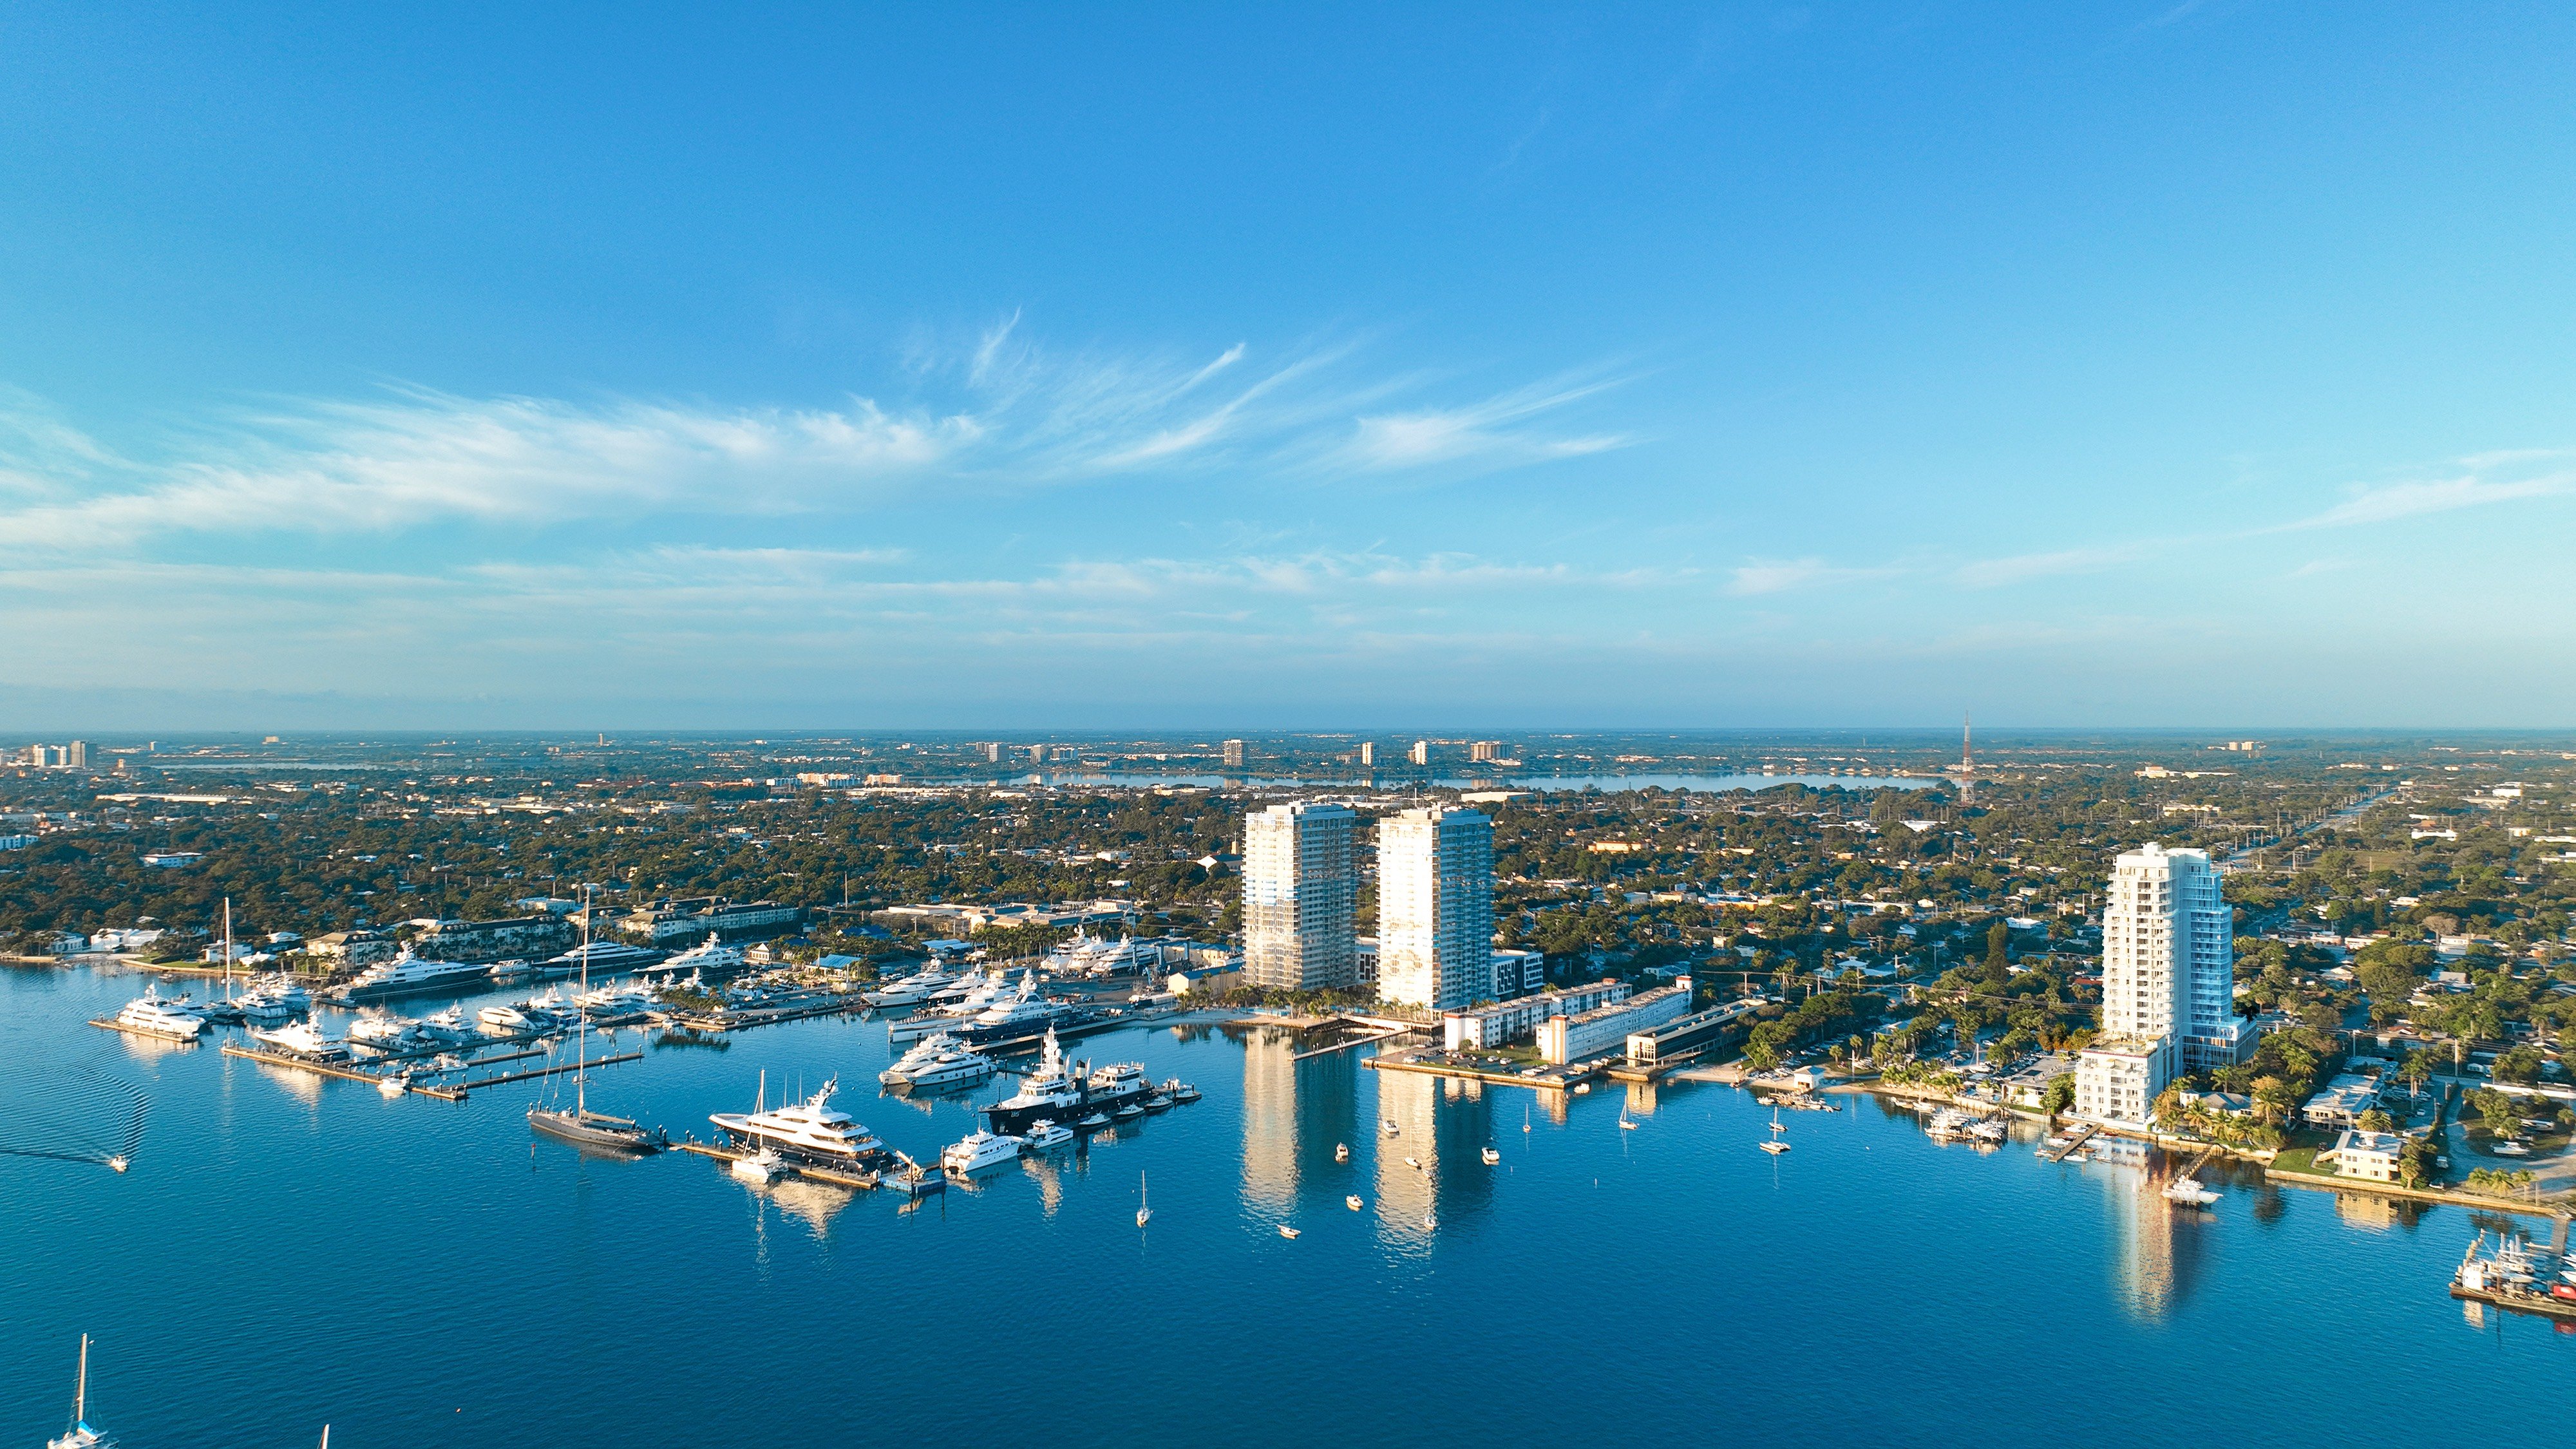
For a buyer considering Alba West Palm Beach, discretion deserves the same attention as the residence itself. The ownership experience extends beyond who may enter to who may see resident information, how access permissions change, and what happens to records once their purpose has ended.
Alba’s public website terms prohibit harvesting personally identifiable information, including account names, from its online services. That provision is not a resident-data policy: it establishes neither the building’s cybersecurity architecture nor its access-log retention periods. Buyers should not read it as confirmation of particular vendors, hosting arrangements, encryption, or multifactor authentication.
Request written policies before closing or move-in. The questions below form a due-diligence framework, not a description of Alba’s deployed systems. For West Palm Beach buyers, the objective is clear responsibility-not an impressive inventory of technology.
Begin with governing documents, access-control rules, privacy notices, and written retention schedules. Ask which entity controls each category of information and which parties may access it. Counsel should assess the obligations of the association, developer, management company, and technology vendors separately; their responsibilities should not be assumed identical.
Distinguish ownership records from operational security information. Where applicable, ask about credential records, visitor registrations, garage entries, elevator events, and camera footage. For each category, request its purpose, authorized viewers, retention period, and disposal process.
Buyers also considering Forté on Flagler West Palm Beach can use the same questions without assuming equivalent systems or policies. Written answers offer a more meaningful comparison than broad assurances about privacy.
Access control involves more than issuing a credential. Ask who authorizes it, what permissions it carries, and how those permissions end. Request the procedures for a departing resident, a lost credential, and a visitor whose authorization has expired.
Second-home buyers should also clarify how temporary access would be managed for household staff, family members, or service providers. Ask whether permissions can be limited to their intended purpose and who reviews outstanding authorizations. These are recommended questions, not confirmed Alba features.
For cybersecurity, request a policy-level explanation of administrator access, authentication, vendor oversight, and incident escalation. Ask whether encryption and multifactor authentication are used rather than presuming they are. Buyers need accountable governance, not technical details that could compromise security. A named contact and a written revocation procedure are useful requests before occupancy.
Florida condominium law generally requires association official records to be maintained within Florida for at least seven years, subject to record-specific exceptions. Some records require permanent retention. Seven years is therefore neither a universal deletion deadline nor a blanket retention period for every door-entry event.
Classification is the central question. Counsel should determine which rules apply to each record rather than automatically extending an official-records requirement to every operational log. A buyer-facing retention framework should distinguish three categories:
Ownership and association records: Determine which official-records obligations apply, including any permanent-retention requirements.
Routine security logs: Request the written schedule for each relevant system without assuming a standard number of days.
Incident evidence: Clarify when preservation overrides routine deletion and who authorizes that change.
For a Palm Beach buyer, the strongest answer is not necessarily the longest retention period. It is a documented explanation of why information is retained, who controls it, and when lawful disposal becomes appropriate.
Ownership does not grant unrestricted access to every resident’s information. Association-records inspection rights are subject to exclusions that protect personal information and electronic security measures.
Protected information includes Social Security numbers, driver-license numbers, credit-card numbers, email addresses, telephone numbers, and emergency-contact information, subject to statutory exceptions. Names, unit designations, mailing addresses, and property addresses used for association notice requirements are not protected in the same way.
The practical consequence is separation or redaction. The right to inspect a record should not be treated as permission to disclose every field it contains. Ask how management separates accessible material from protected information and who reviews the response before release.
For buyers weighing Mr. C Residences West Palm Beach alongside Alba, this offers another useful comparison: how clearly does the written process reconcile owner access with resident privacy? The question does not presume any project’s answer.
Camera footage and access-control logs can provide contemporaneous evidence. When litigation is reasonably anticipated, preserving that evidence before routine deletion becomes an important consideration.
Ask how an incident is brought to the attention of the person authorized to preserve relevant records. The procedure should address the applicable time window, relevant systems, and preservation responsibilities without turning an incident request into unrestricted access to unrelated residents’ movements.
Distinguish preservation from disclosure. Keeping material available for a legal matter does not automatically make it inspectable by every owner. Counsel should guide the scope of preservation and any subsequent release. The goal is to retain relevant evidence while respecting the protections that continue to apply.
Florida’s data-breach law addresses unauthorized access to electronic data containing personal information, subject to its definitions and exceptions. For a breach affecting at least 500 individuals in Florida, a covered entity generally must notify the Department of Legal Affairs as soon as practicable and within 30 days after determining, or reasonably believing, that a breach occurred.
That threshold concerns department notification. Affected individuals must also receive notice when the separate individual-notification requirements apply. Buyers should not assume that a smaller incident is exempt from notification obligations.
The five-year documentation requirement is narrower than a general breach-record retention rule. It applies specifically to a determination that individual notification is unnecessary because the breach has not caused, and will not likely cause, identity theft or other financial harm.
Finally, covered entities and third-party agents must take reasonable measures to dispose of customer records containing personal information when retention is no longer needed. Disposal must make that information unreadable or undecipherable. Ask how deletion responsibilities are assigned across management and vendors, with legal review of applicable obligations.
Before move-in, retain the written policies and identify the contact for access changes, privacy concerns, and incident preservation. Revisit those procedures when household permissions change or ownership ends. A clearly explained process offers a firmer basis for confidence than an unsupported promise that everything is secure.
For a discreet approach to your next South Florida residence, explore MILLION.
If branded residences are on your mind — as a home or as an allocation — we would be glad to share what we are seeing, privately.
Begin a quiet conversationNo. The terms prohibit harvesting personally identifiable information from online services, but do not establish building cybersecurity practices or access-log retention periods.
Request governing documents, access-control rules, privacy notices, and written retention schedules. Ask which entity is responsible for each category of resident information.
The official-records rule does not establish a blanket seven-year period for every access-control log. Counsel should assess record classification and applicable requirements.
No. Some condominium records require permanent retention, and record-specific exceptions mean seven years is not a universal deletion deadline.
No. Inspection rights are subject to exclusions for protected personal information and electronic security measures, and records may require separation or redaction.
No. Names, unit designations, and addresses used for association notices are not protected in the same way as the statute’s excluded personal information.
Ask who revokes credentials, how quickly revocation occurs, and how outstanding authorizations are reviewed. These are due-diligence questions, not verified Alba procedures.
When litigation is reasonably anticipated, relevant footage and logs may need preservation before routine deletion. Counsel should guide the preservation scope and any disclosure.
No. It concerns notification to the Department of Legal Affairs; affected individuals must also receive notice when the separate individual-notification requirements apply.
Covered entities and third-party agents must take reasonable disposal measures when customer records no longer need retention. Personal information must be made unreadable or undecipherable.