A discreet buyer’s briefing on the distinction between brand-level privacy policies and building-level controls at St. Regis Residences Brickell, with practical questions about guest profiles, vendor access, smart-home systems, and contractual accountability.
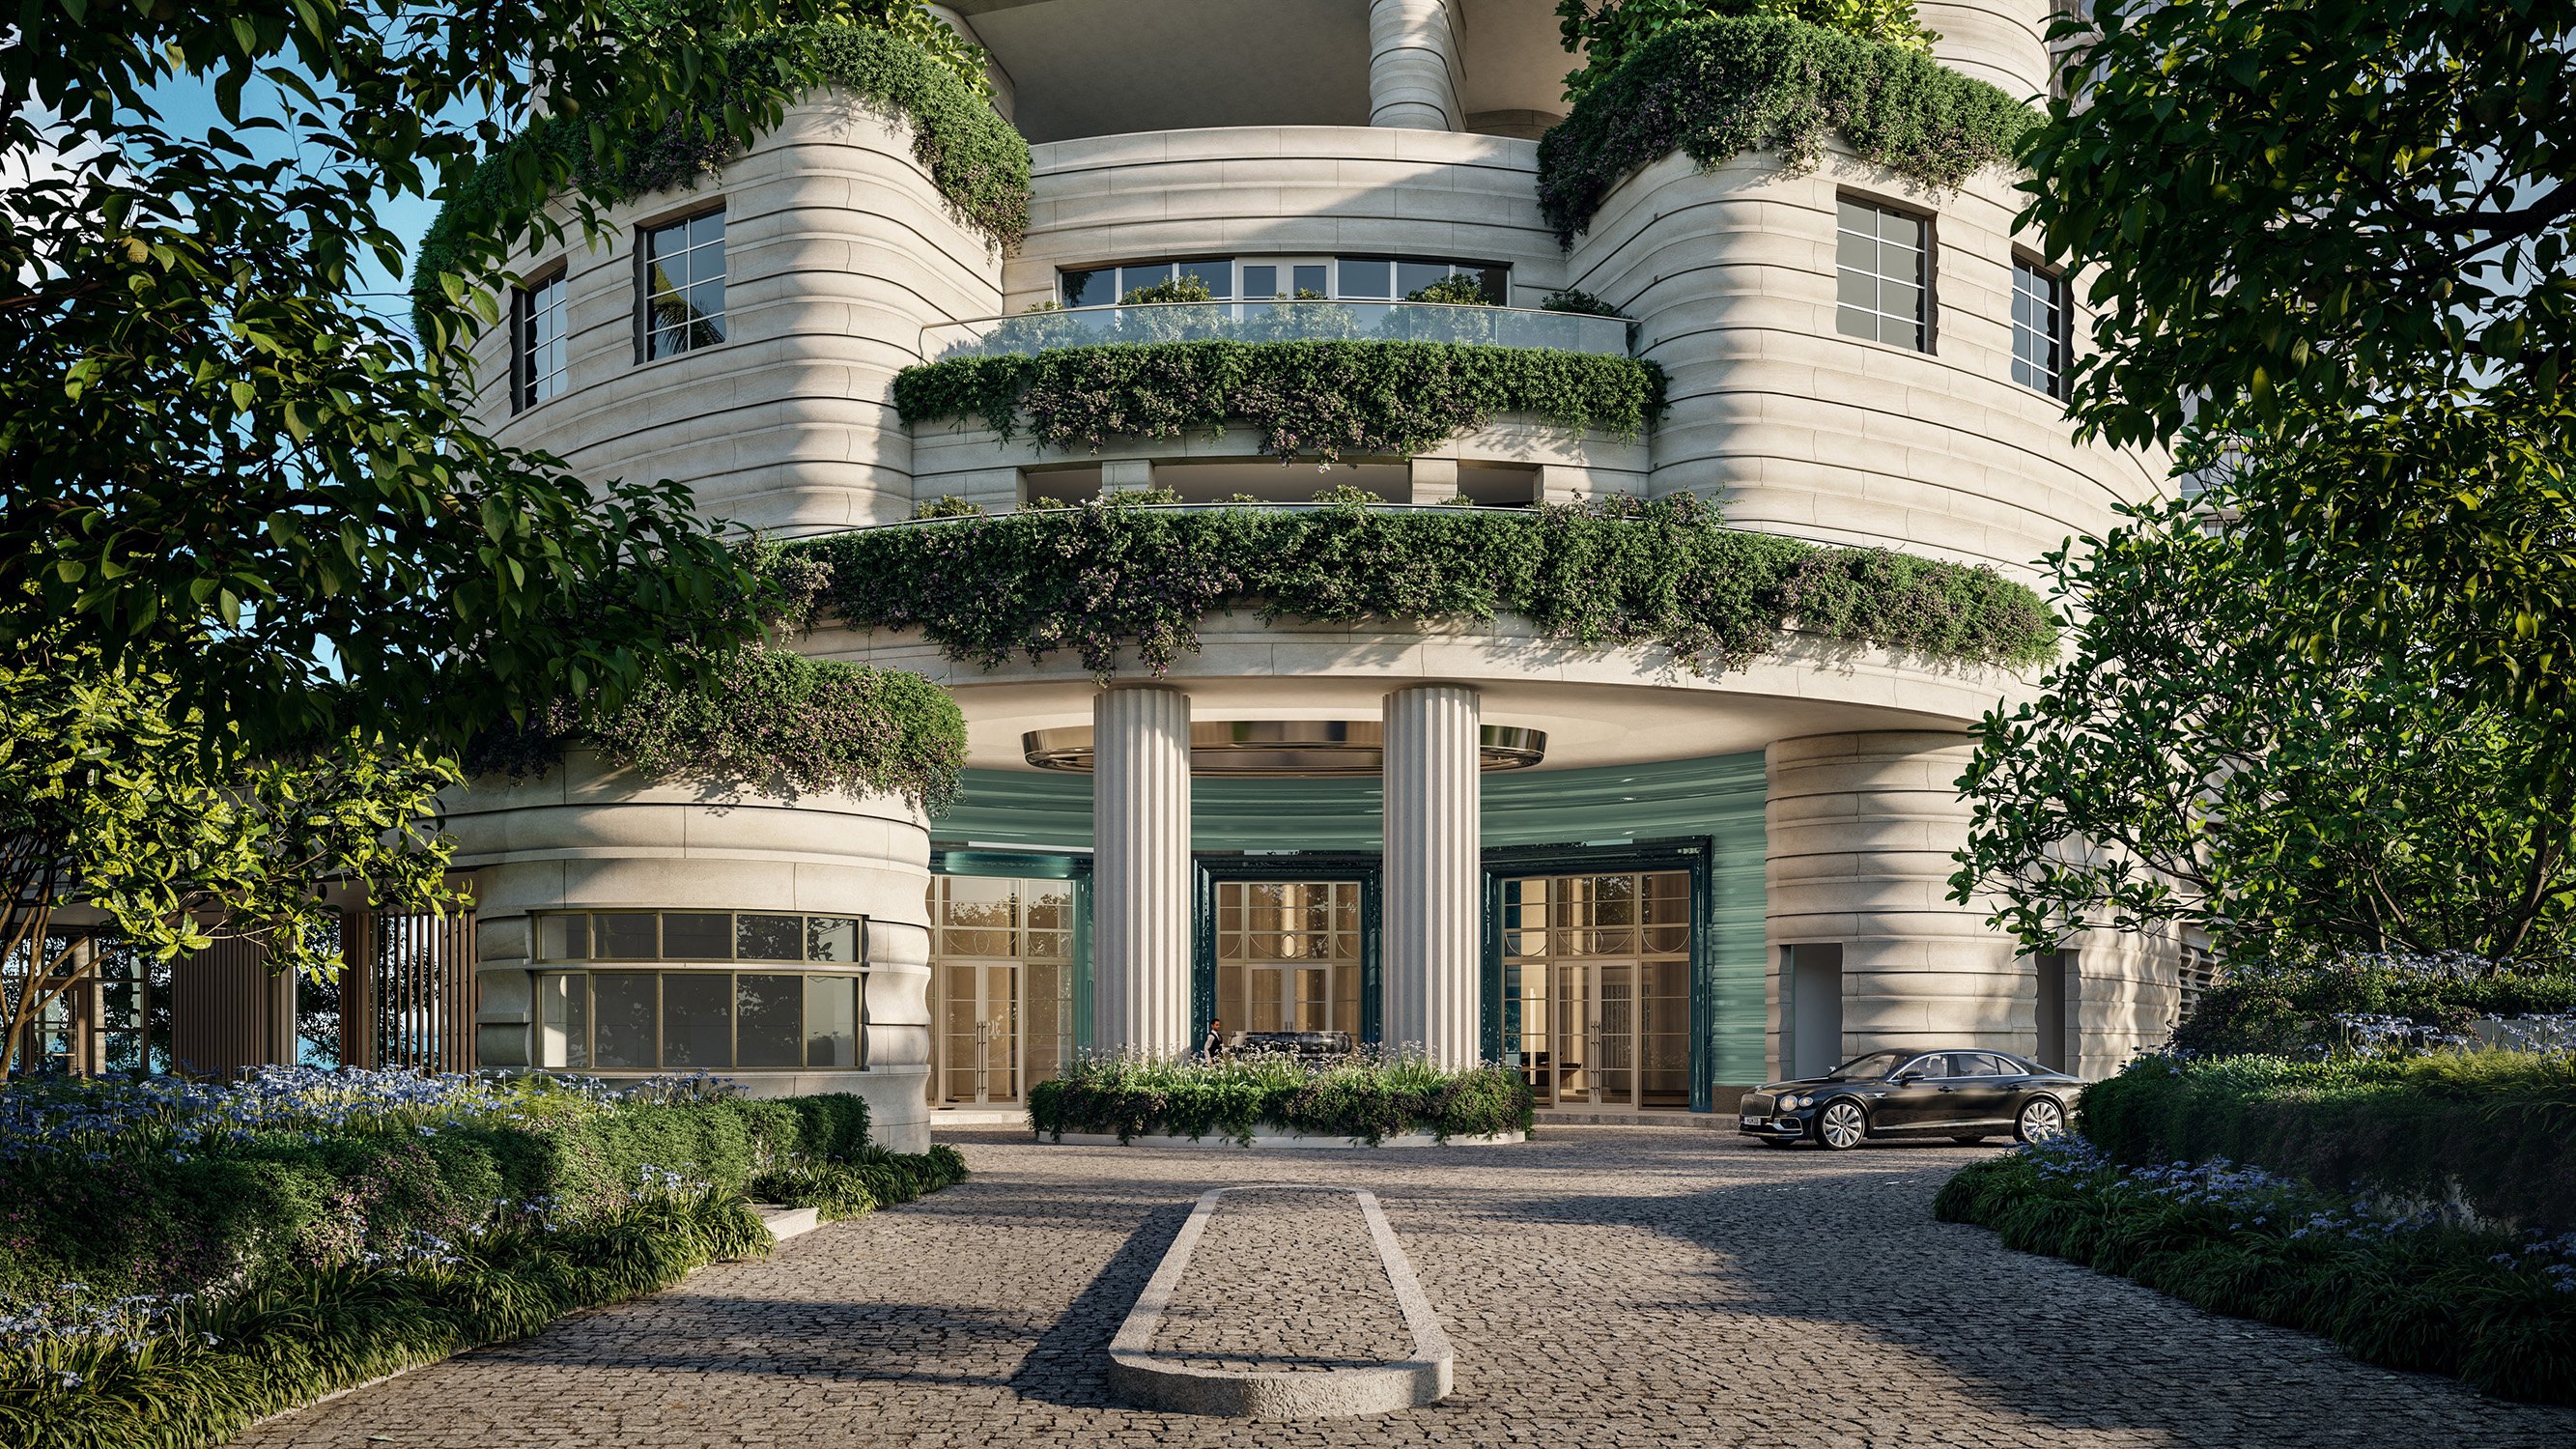
For a private client considering St. Regis® Residences Brickell, discretion deserves the same attention as architecture and service. The question is not simply whether information is protected, but who receives it, how they may use it, and which obligations remain enforceable after purchase.
The essential distinction is between published privacy language and the controls governing a particular residence. General safeguards can describe an organization’s approach without establishing how a condominium’s access systems, concierge records, or connected devices are configured. Branding alone does not resolve that distinction.
A sound private-client briefing separates three layers: information submitted during the sales process, information processed through any hospitality-related relationships, and information generated through residential operations. Buyers should not assume those layers share one controller, one retention schedule, or one route for privacy requests.
Start by requesting the privacy terms applicable to the sales website and inquiry process. Identify the party responsible, the information covered, permitted recipients, and the safeguards described. Then ask which separate documents would govern information collected after an owner takes possession.
A sales-inquiry policy is not a building-specific cybersecurity audit. Even language describing technical, physical, and administrative safeguards does not establish how every residential system or vendor operates. Ask for evidence relevant to the systems the household would actually use.
If hospitality-related services are proposed, request the applicable terms and clarify whether they cover residents, visitors, or only particular service interactions. Do not infer that a hospitality brand operates the condominium’s resident-facing systems or that branding establishes an on-site hotel.
The objective is a clear map of contractual and operating responsibilities. A purchaser should be able to distinguish a general policy statement from a documented obligation that applies to a specific service.
Privacy documents can use familiar words in unfamiliar ways. A defined term such as “Owners” should be checked against the document’s definitions rather than assumed to mean individual condominium purchasers. Ask whether it refers to property-owning entities, management counterparties, or residents.
For every proposed disclosure of personal information, identify the recipient’s role and permitted purpose. Where developers, associations, managers, brand counterparties, or vendors are involved, distinguish who decides how information is used from who processes it on another party’s behalf.
For buyers also considering Cipriani Residences Brickell, the same diligence principle applies: establish responsibility independently of brand appeal. This is a purchasing discipline, not a comparison of either project’s cybersecurity performance.
Request a written explanation of each applicable party’s responsibilities. It should also identify where a resident directs questions, requests, and complaints when several organizations participate in delivering a service.
Personalization and privacy are not necessarily opposing goals. The important question is whether information needed to fulfill a request remains confined to that purpose or also feeds broader profiling, communications, or analytics.
Ask whether a resident profile would connect to a hospitality or loyalty profile, whether visitor details would enter the same environment, and which parties could retrieve either record. Establish what is mandatory for service and what, if anything, is optional.
Request specific answers about preference histories, visitor information, marketing communications, and affiliated-entity sharing wherever relevant. Do not assume profiling or recognition technologies are used, or that any optional uses can be switched off, without confirmation.
For a household seeking a discreet lifestyle, the practical objective is information proportionate to service. Preferences can support convenience, but the buyer should understand whether they persist, travel between systems, or remain available after the original request ends.
If smart-home technology or resident-facing digital services are proposed, a marketing description alone does not establish vendor identities, encryption standards, retention periods, or management access to device data. Treat it as a reason to ask precise questions rather than evidence of a particular security architecture.
Begin with a system inventory. For any resident app, entry platform, concierge tool, parking system, amenity-booking service, or smart-home component proposed for use, request the controller, vendor, information collected, authorized users, and deletion rules. Establish which systems actually apply before evaluating their controls.
For cybersecurity, request written explanations of administrator authentication, access permissions, encryption, remote support, security updates, and access logging. These are recommended diligence questions, not confirmed project features. Ask how vendor access is approved and withdrawn, particularly when personnel or management arrangements change.
The same review is worth requesting when evaluating The Residences at 1428 Brickell. A technology description should translate into responsibilities a purchaser can understand, without assumptions about that project’s implementation.
Data retention deserves a separate conversation. Request written schedules for surveillance footage, visitor records, entry logs, valet information, and device telemetry wherever those categories are collected. Ask whether deletion reaches vendor-held copies and which exceptions preserve records for legal or operational reasons.
Secondary use should be equally explicit. Determine whether vendors may use information for analytics, advertising, or AI applications, and whether any permissions can be declined without compromising essential services. Silence in a marketing description is neither a prohibition nor permission.
Request system-specific details about hosting locations, remote access, and any international processing or transfer arrangements. Do not assume a general brand policy establishes where the building’s particular databases are hosted or who can access them.
Finally, establish who leads incident response, who informs affected residents, and who coordinates vendors. Ask how residents receive assistance and how responsibilities are maintained through changes in management. These obligations should be documented, not assumed to follow the brand hierarchy.
For a purchase under consideration, seek governing provisions addressing resident information, surveillance, guest records, vendor access, and breach notification wherever applicable. Review them with counsel alongside the proposed service relationships.
Whether the shortlist includes this residence or Una Residences Brickell, the strongest diligence outcome is a clear allocation of responsibility, not an assurance of absolute security. Ask which access, correction, deletion, and restriction requests are available, who handles them, and what legal or operational limits apply.
The private-client standard is simple: service should feel seamless, while information handling remains explainable and accountable.
For a discreet perspective on South Florida residential choices, explore MILLION.
If branded residences are on your mind — as a home or as an allocation — we would be glad to share what we are seeing, privately.
Begin a quiet conversationNo. Buyers should identify the actual operator and responsible party for each residential database or technology platform.
Request the applicable website privacy terms and identify the responsible party named there. Separately confirm who would handle information collected during residential operations.
No. General information-handling commitments do not establish the configuration or security performance of the condominium’s systems.
No. Check the document’s definitions and ask which entities or individuals the term covers.
No. Confirm the proposed operating arrangements rather than inferring a hotel or hospitality operator from the brand name.
Ask whether resident and visitor records connect to hospitality profiles, who can retrieve them, and which uses are optional.
No. Request system-specific documentation covering vendors, encryption, remote access, and management permissions wherever applicable.
Request written rules for any collected surveillance footage, visitor records, access logs, valet information, and device telemetry. Clarify whether those rules also cover vendor-held copies.
Ask where each applicable system hosts information and whether access or processing occurs outside the United States. Request details of any relevant transfer arrangements.
Ask the relevant responsible party which requests are available and how to submit them. Availability and exceptions depend on the applicable terms, law, and information involved.