A buyer’s guide to verifying Arte Surfside’s digital privacy protections, from staff and vendor permissions to surveillance access, retention schedules, and resident-data deletion.
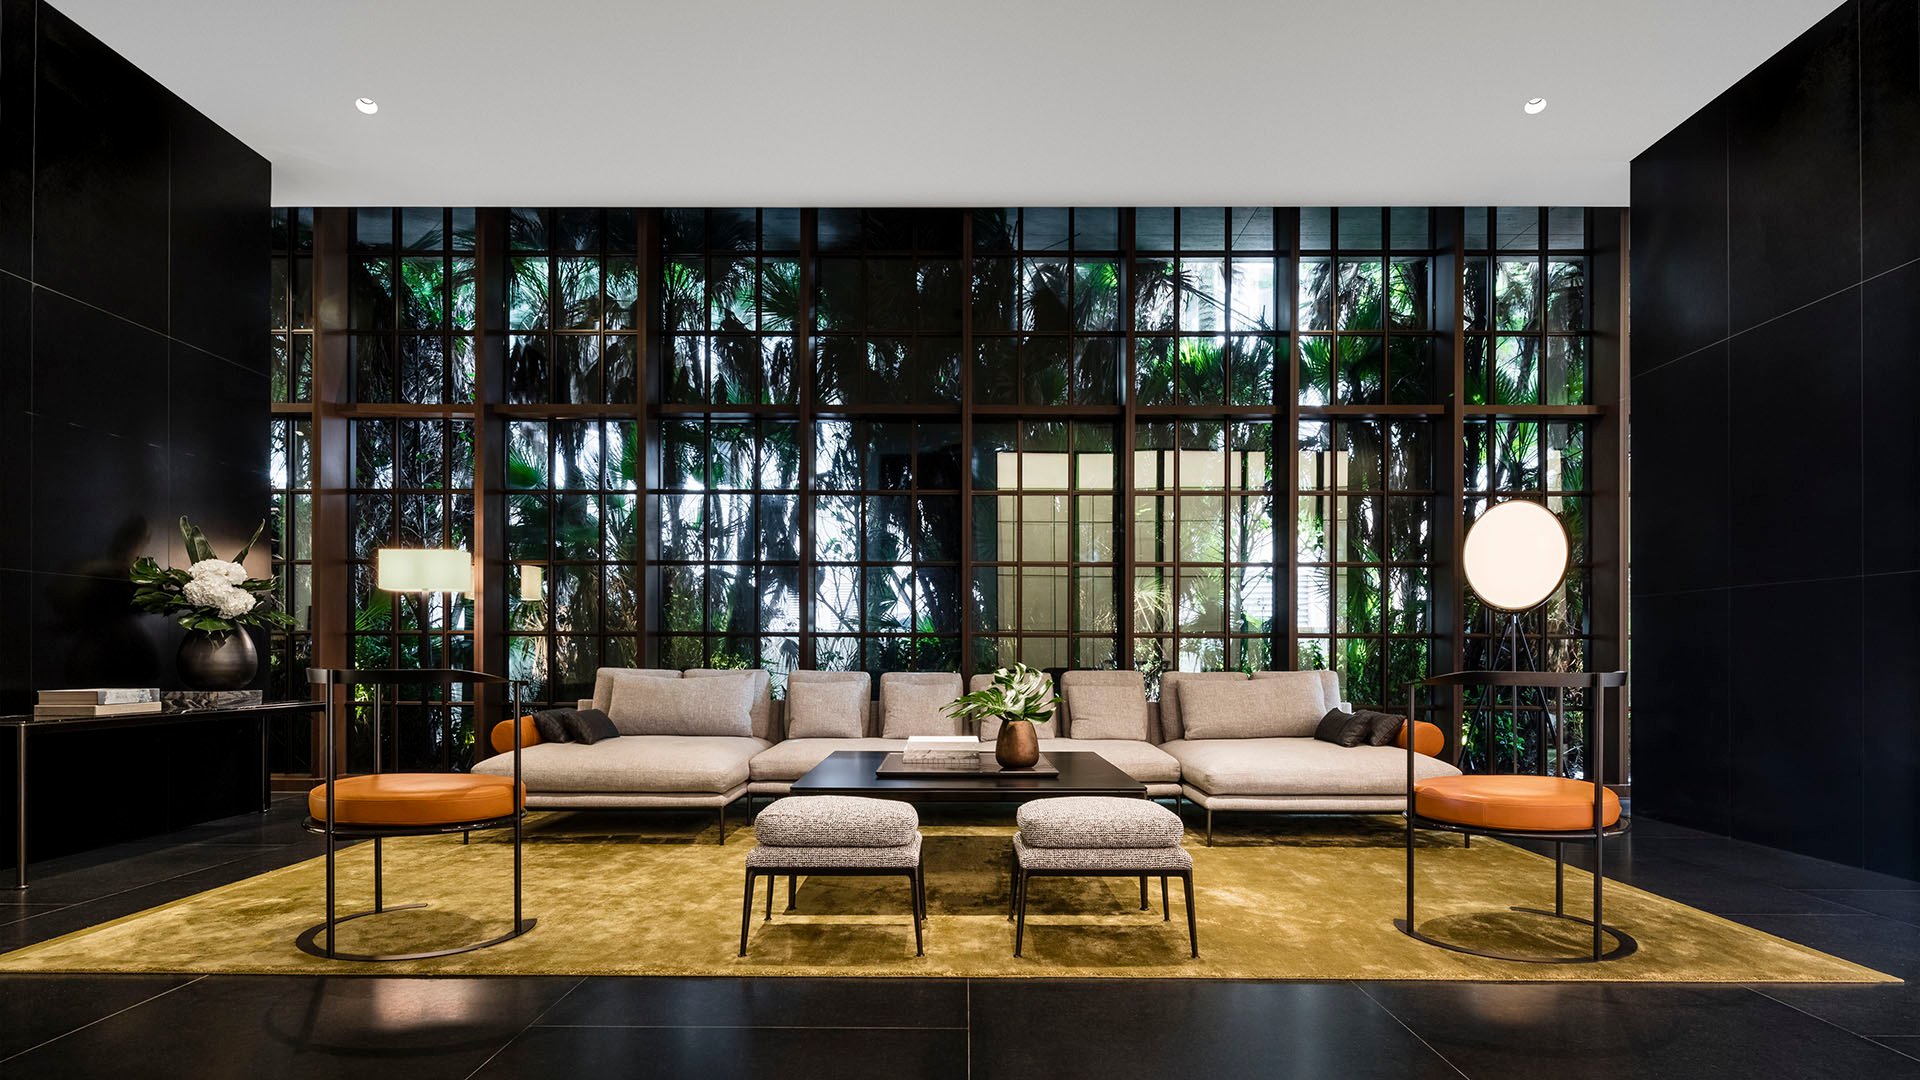
At Arte Surfside, the oceanfront address at 8955 Collins Avenue, Surfside, Florida 33154, places privacy in a highly personal residential setting. For a buyer, however, discretion warrants scrutiny beyond the arrival experience. The essential questions are who can access resident information, how that access is recorded, and when records are deleted.
The advertised service program includes 24-hour security and valet, residential butlers, a lifestyle concierge, and a general manager. These are physical security and service offerings, not cybersecurity certifications. Confirm the current program with management rather than treating the original offering as a statement of present operations.
Arte’s actual cybersecurity architecture, vendor identities, access-log retention periods, and deletion practices are not established here. Treat them as diligence questions, not evidence of a deficiency. The objective is a documented understanding of privacy before purchase.
Begin with written cybersecurity policies covering passwords, association communications, personal devices, vendor access, and incident escalation. Ask who maintains these policies, who approves changes, and how staff are informed of their responsibilities. A general assurance that systems are secure should prompt a request for supporting documentation.
Next, request a suitably redacted system-access register. It should identify the roles with logins, the systems those roles can access, and whether multi-factor authentication is enabled. Ask specifically about administrative permissions, outside support access, and the procedure for revoking access when employment or a vendor relationship ends.
Buyers do not need passwords, live credentials, or sensitive network diagrams. Request enough evidence to understand accountability without exposing the building’s defenses. If detailed records cannot be shared, ask whether a qualified adviser can review them confidentially and summarize the relevant controls.
A personal service program deserves equally precise data boundaries. Ask which resident details are collected for concierge, valet, guest, and household-service requests, if those functions use digital records. Establish whether that information remains within association-managed systems or also passes to outside providers.
Request a description of how association communications are stored. Discuss centralized records and association-controlled email, particularly where staff or board members might otherwise use personal accounts. Ask who can retrieve archived messages and how access changes after a departure.
For buyers also considering The Surf Club Four Seasons Surfside, apply the same service-and-data questions independently. This is a comparison framework, not a claim that either property uses a particular platform or follows the same privacy practices.
Ask management to identify the providers that store or process resident information and explain their responsibilities. Review relevant contract provisions for security standards, data handling, breach notification, and incident-response responsibilities. Clarify who communicates with residents if a vendor discovers a problem.
Request security evidence appropriate to each provider’s role. Areas to examine include data-center safeguards, security audits, vulnerability assessments, multi-factor authentication, access logging, and disaster recovery. These are items to verify, not established protections at Arte.
Also request the incident-response plan and an explanation of backup arrangements, including defined storage locations. Who coordinates a response, and who can authorize restoration? Confirm how the association and its vendors divide those duties. Contract commitments and operational procedures should reinforce one another, not leave responsibility ambiguous.
Do not assume access-control records follow a universal retention period. Request the actual schedule for each system in use, along with an explanation of what each event records. Ask whether entries identify an individual credential, a location, a timestamp, or additional information, and who can search or export them.
The most useful review separates four issues:
Collection: What information is generated, and for what purpose?
Permissions: Which staff, board roles, or vendors can view or export it?
Retention: How long does each record category remain available?
Preservation: What prevents deletion when a legal obligation requires it?
A seven-year association-records framework is not proof that Arte retains every access event for seven years. Have counsel evaluate record classification and applicable requirements. A shorter internal policy does not override the law, and a longer retention period should still have a stated purpose.
Request the written camera policy, relevant vendor contract, and adopting board resolution. Ask which roles may view live feeds, retrieve recordings, or provide copies, and what approval is required. The inquiry concerns governance, not the circulation of sensitive footage.
Then examine the audit trail for surveillance access. Ask whether each viewing records the user, date, camera, and reason. A camera recording documents what occurred within its field of view; a viewing log documents who accessed that material. These are not interchangeable records.
Counsel should assess inspection rights and privacy rules for each category separately. Likewise, buyers comparing Fendi Château Residences Surfside should request that property’s own documentation. Neither a shared location nor similar purchase criteria establish equivalent surveillance governance.
Access logs are only one part of the retention discussion. Ask for a resident-data inventory and a category-specific schedule covering the information the association actually holds. Potential categories to clarify include contact details, guest authorizations, service requests, and association communications; their inclusion here does not establish Arte’s collection practices.
Ask what happens when an owner sells, a guest authorization expires, or a vendor contract ends. Does access stop promptly? Are active records deleted, archived, or retained for a defined obligation? How are exported copies and backups addressed?
Request a written explanation of deletion exceptions and preservation requirements. Avoid demanding immediate erasure as a blanket condition: counsel should determine what must remain available and why. The goal is a clear information lifecycle, with responsibility assigned at every stage.
Turn the discussion into a concise document request and a list of unresolved questions. Prioritize written policies, a redacted permissions register, vendor protections, incident-response and backup arrangements, retention schedules, and camera-governance records. Ask management to distinguish current practices from planned improvements.
Have counsel assess which materials a prospective buyer can obtain, which may require seller cooperation, and which warrant confidential specialist review. Do not assume owner inspection rights grant buyers unrestricted access to security-sensitive or personal information.
If an answer remains unclear, seek clarification rather than infer either safety or failure. A well-informed purchase rests on documented responsibilities, appropriate access, and a defensible retention policy-not the visibility of the security desk alone.
For a discreet conversation about your South Florida property search, connect with MILLION.
If branded residences are on your mind — as a home or as an allocation — we would be glad to share what we are seeing, privately.
Begin a quiet conversationArte Surfside is an oceanfront condominium at 8955 Collins Avenue, Surfside, Florida 33154.
No. The published security and valet offering describes physical security and service, not cybersecurity certification; current operations should be confirmed with management.
Request written policies addressing passwords, communications, personal devices, vendor access, and incident escalation. Also ask for incident-response procedures and backup arrangements.
It should identify who has logins, which systems they can access, and whether multi-factor authentication is enabled. A redacted version can support diligence without exposing credentials.
Review security standards, data-handling responsibilities, breach notification, and responsibility for responding to incidents. Ask for evidence supporting the relevant security commitments.
Arte’s actual retention period is not established here. A seven-year association-records framework does not establish a universal rule for every access event.
Have counsel assess the records’ classification, applicable inspection rights, and privacy restrictions. Do not assume owner inspection rights provide unrestricted access for prospective buyers.
Request the written camera policy, relevant vendor contract, and adopting board resolution. Ask whether surveillance access is logged by user, date, camera, and reason.
No. Recordings capture activity within a camera’s view, while viewing logs document access to that material; counsel should assess their treatment separately.
Ask management to explain access termination, archiving, deletion, and treatment of backups or exported copies. Applicable retention and preservation obligations must be assessed before assuming data can be erased.